On-boarding EasyRadius using Azure Portal
EasyRadius is a SaaS solution delivered through the Microsoft Marketplace and provisioning is integrated into the Azure Portal.
Before you start, make sure you have a certificate authority that issues client certificates to your devices. EasyRadius authenticates certificates — it does not issue them. EasyScep is our SaaS certificate authority for Microsoft Intune and links to EasyRadius during setup, but any CA with a reachable OCSP responder works (see Certificate revocation checking).
Signing up
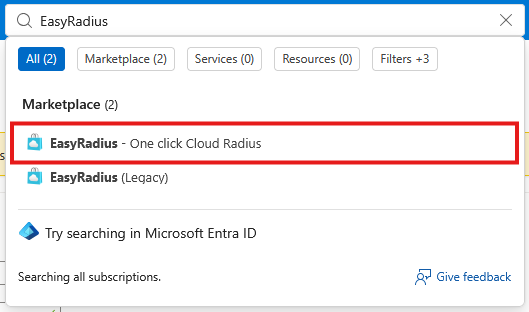
To get started, go to the EasyRadius Azure Marketplace listing here or simply open the Azure Portal and type "EasyRadius" in the top search bar.
When you are in the Azure Portal, you will get this screen where you need to select which subscription and resource group you want to use for provisioning, this is primarily relevant for billing scope.
You will also need to name your EasyRadius instance - we suggest a name like EasyRadius-Production to make it clear what it's for. This is the name the administration portal lists the instance by.
Important: Ensure that the selected plan and renewal setting is correct before continuing
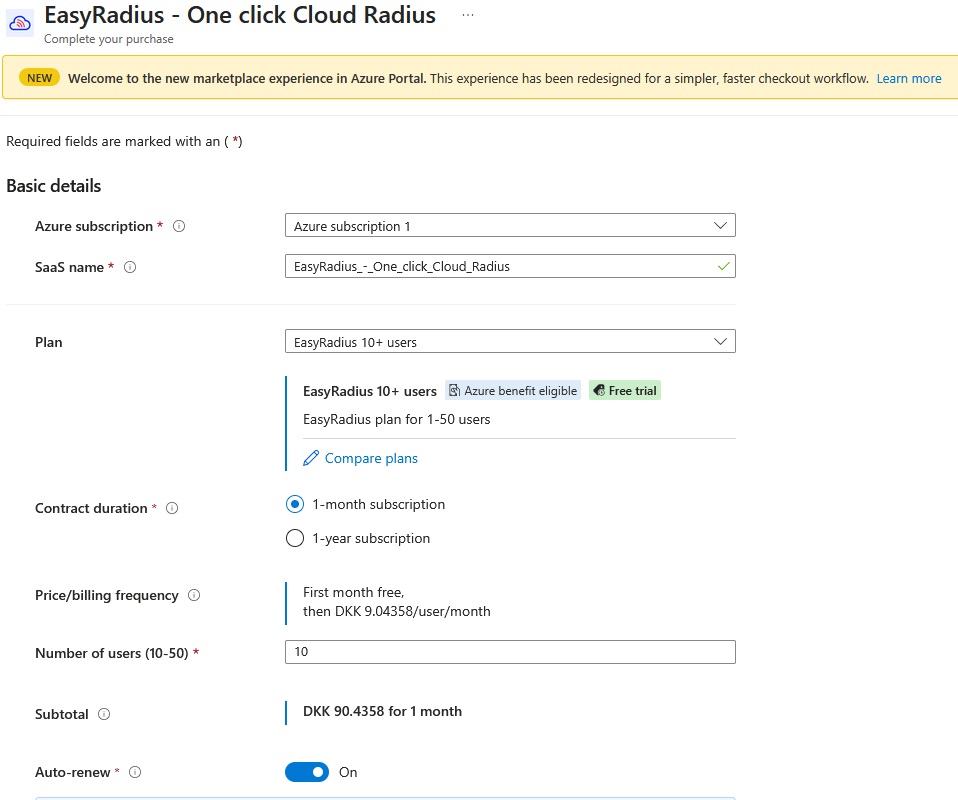
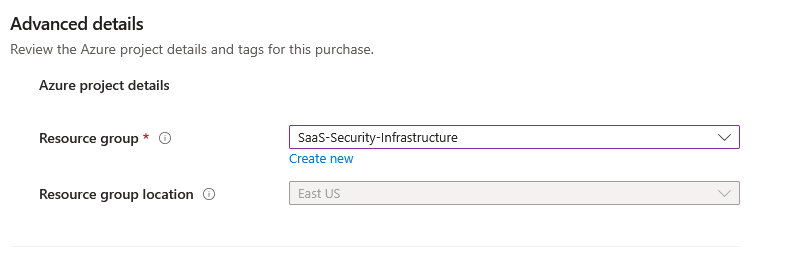
After you have filled in the required information, confirm your settings by clicking "Complete Purchase", now the service is getting provisioned. It typically takes less than 1 minute before you can continue with initial configuration.
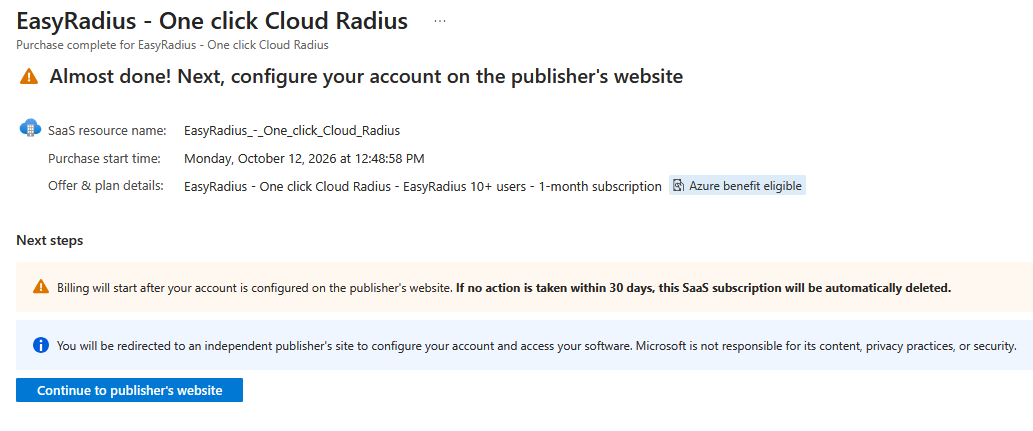
When you see the above screen, you can continue by clicking "Continue to publisher's website". This brings you to the administration portal, where your new subscription is waiting to be set up. Click Configure to start the setup wizard.
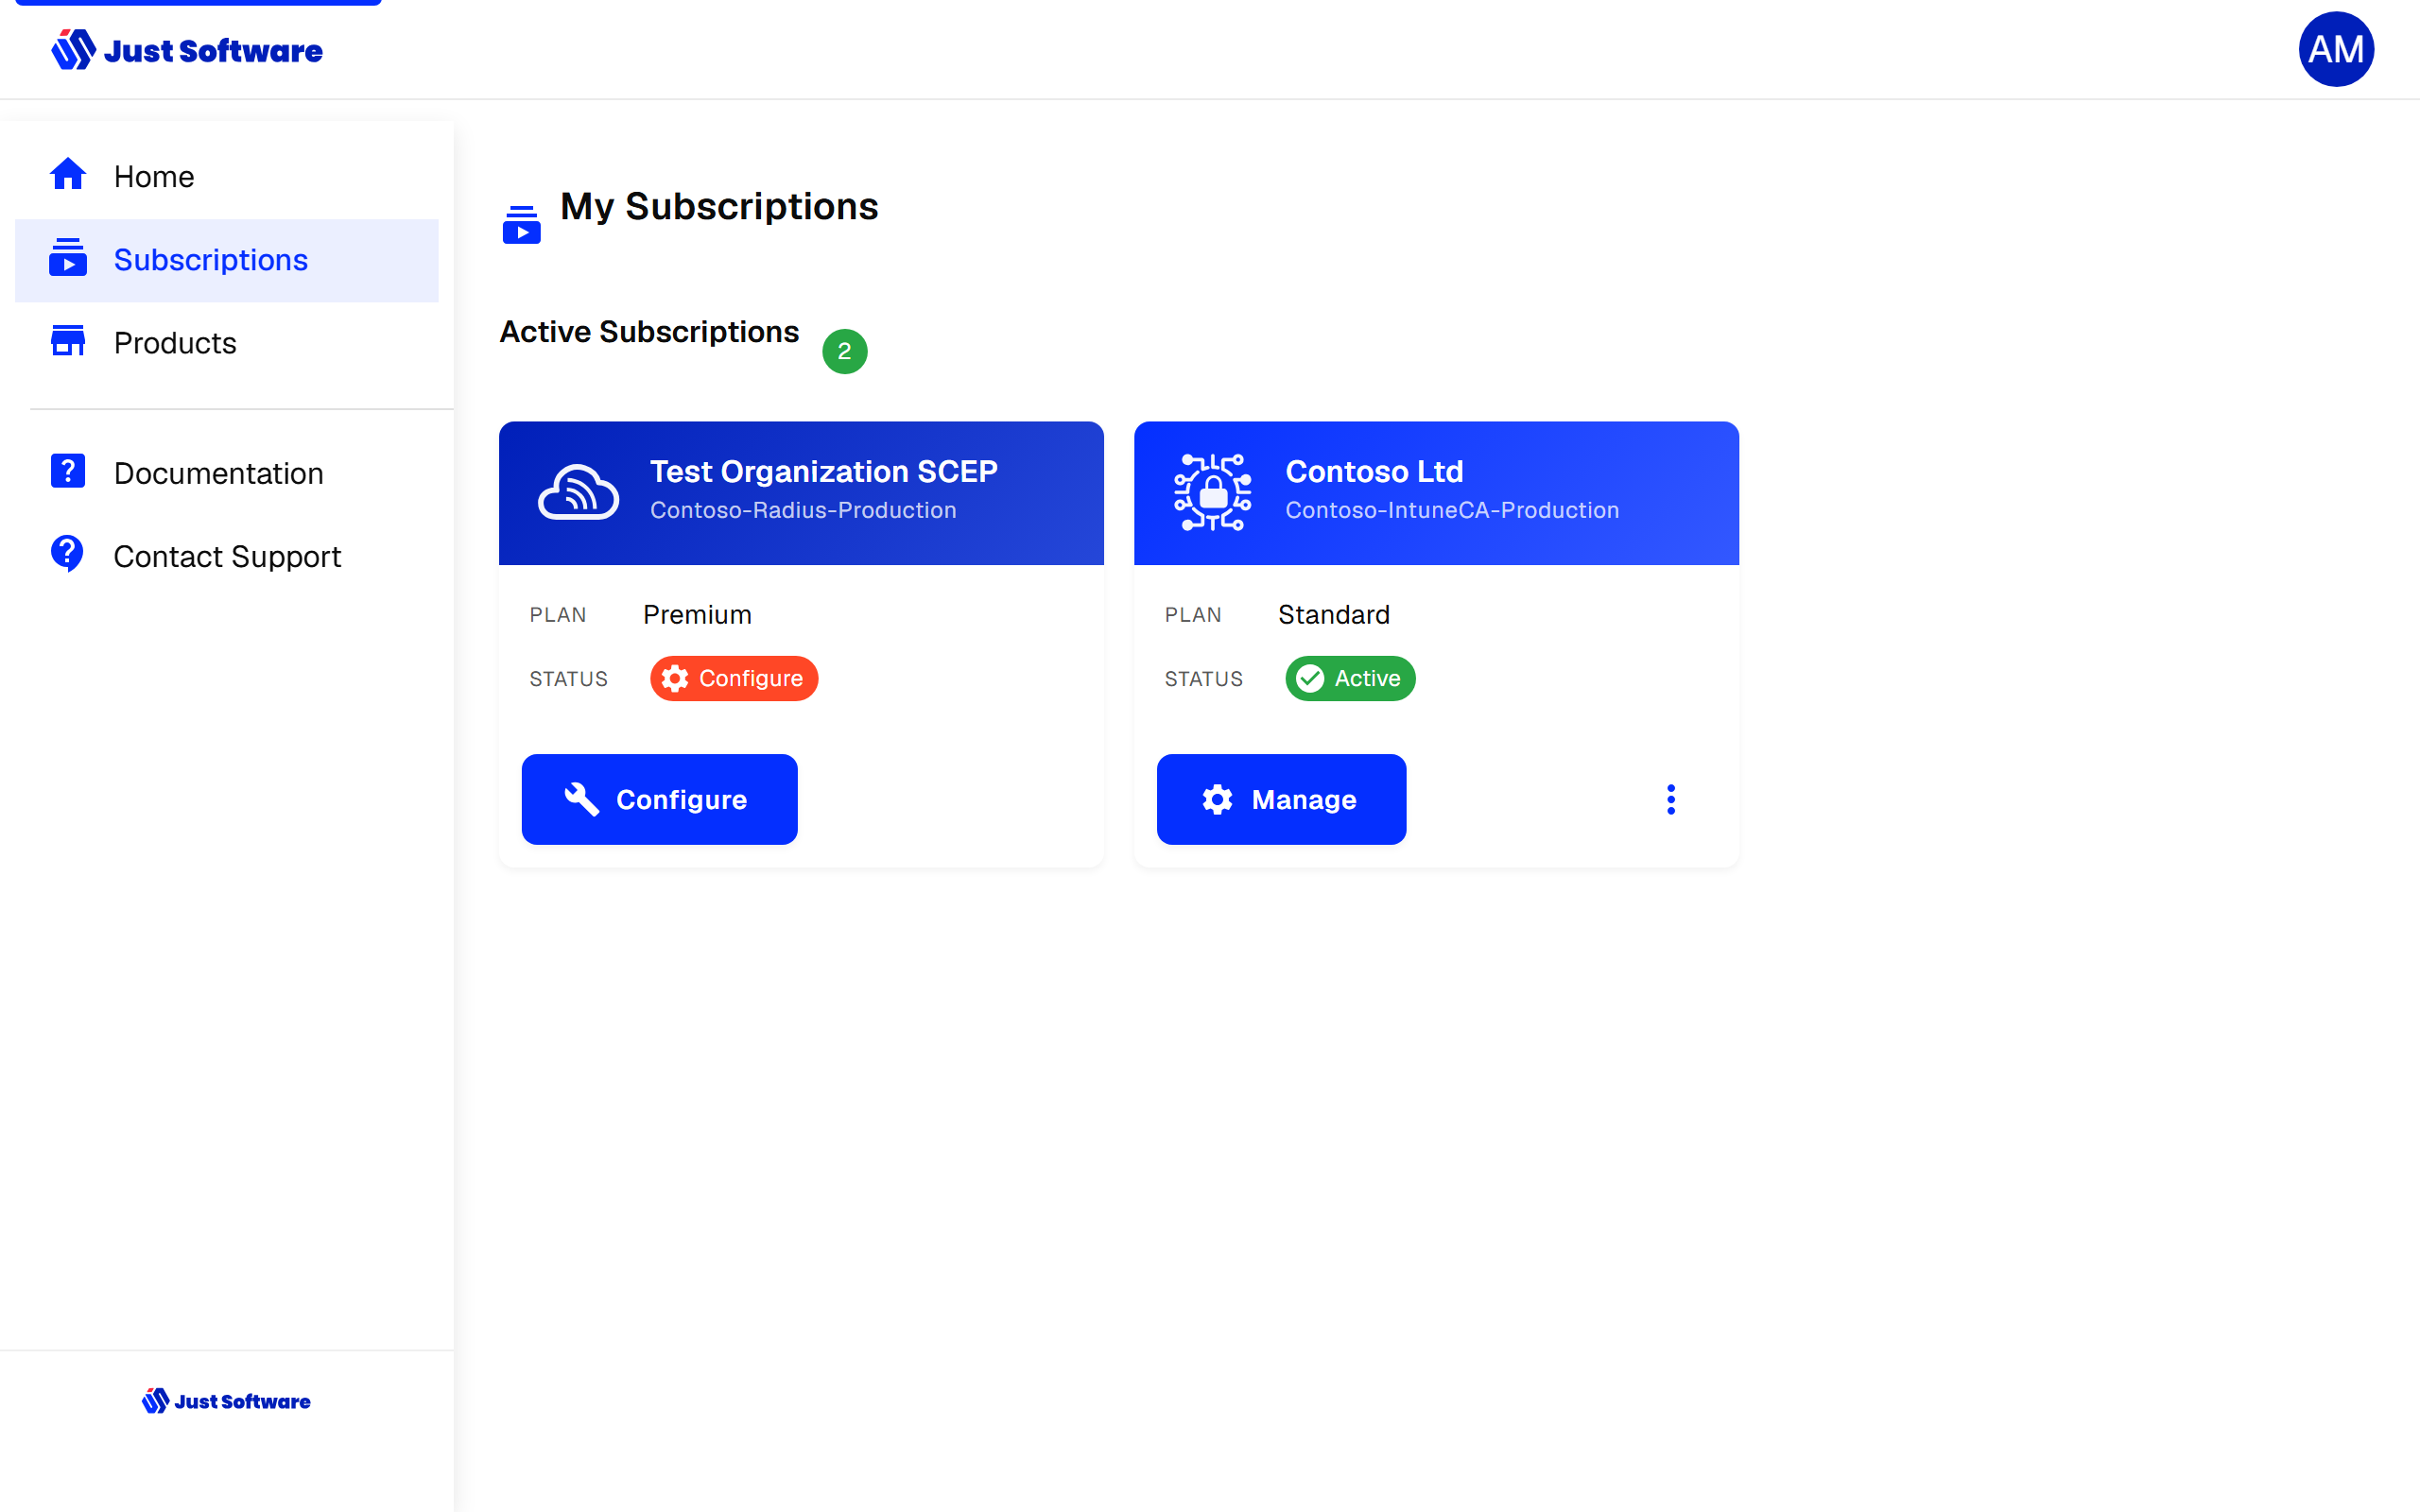
Completing the setup wizard
You need the Owner role on the subscription to run the wizard. The account you sign in with when you arrive from the Azure Portal after the purchase becomes the subscription's first Owner; you can add colleagues afterwards under Access Control.
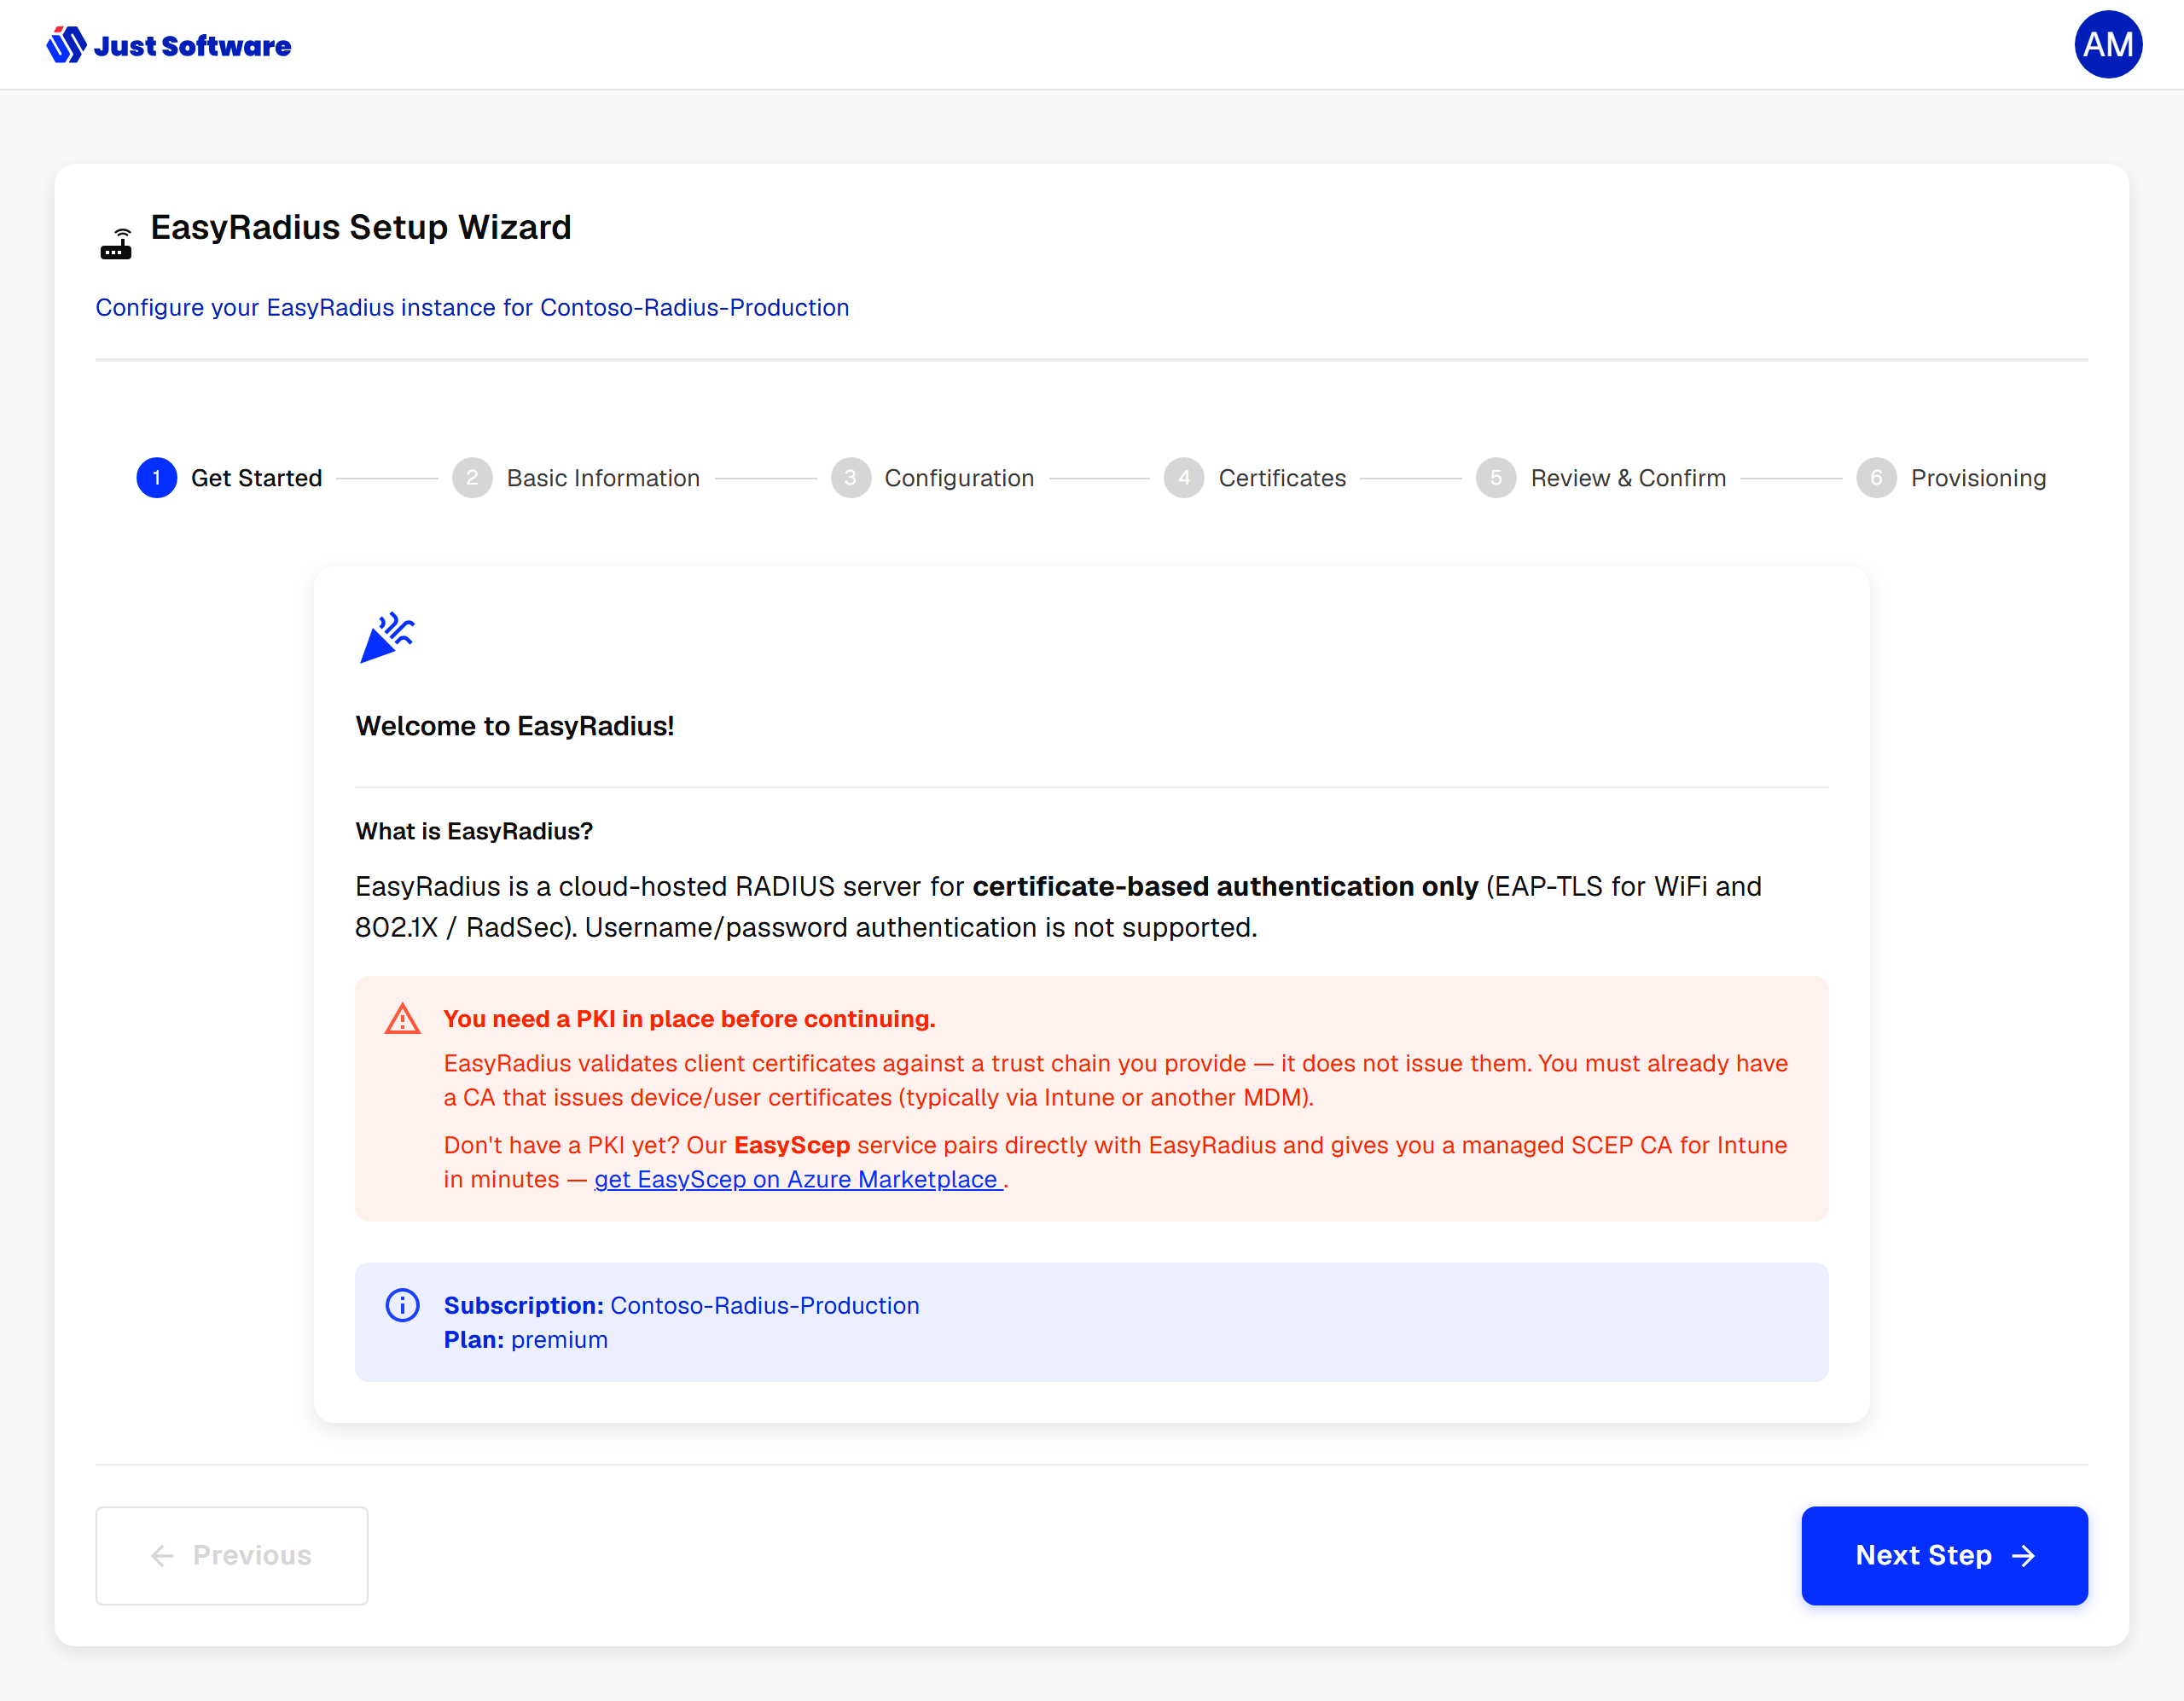
Get Started. The welcome screen summarises what EasyRadius is and what you need before you begin. Click Next Step to continue.
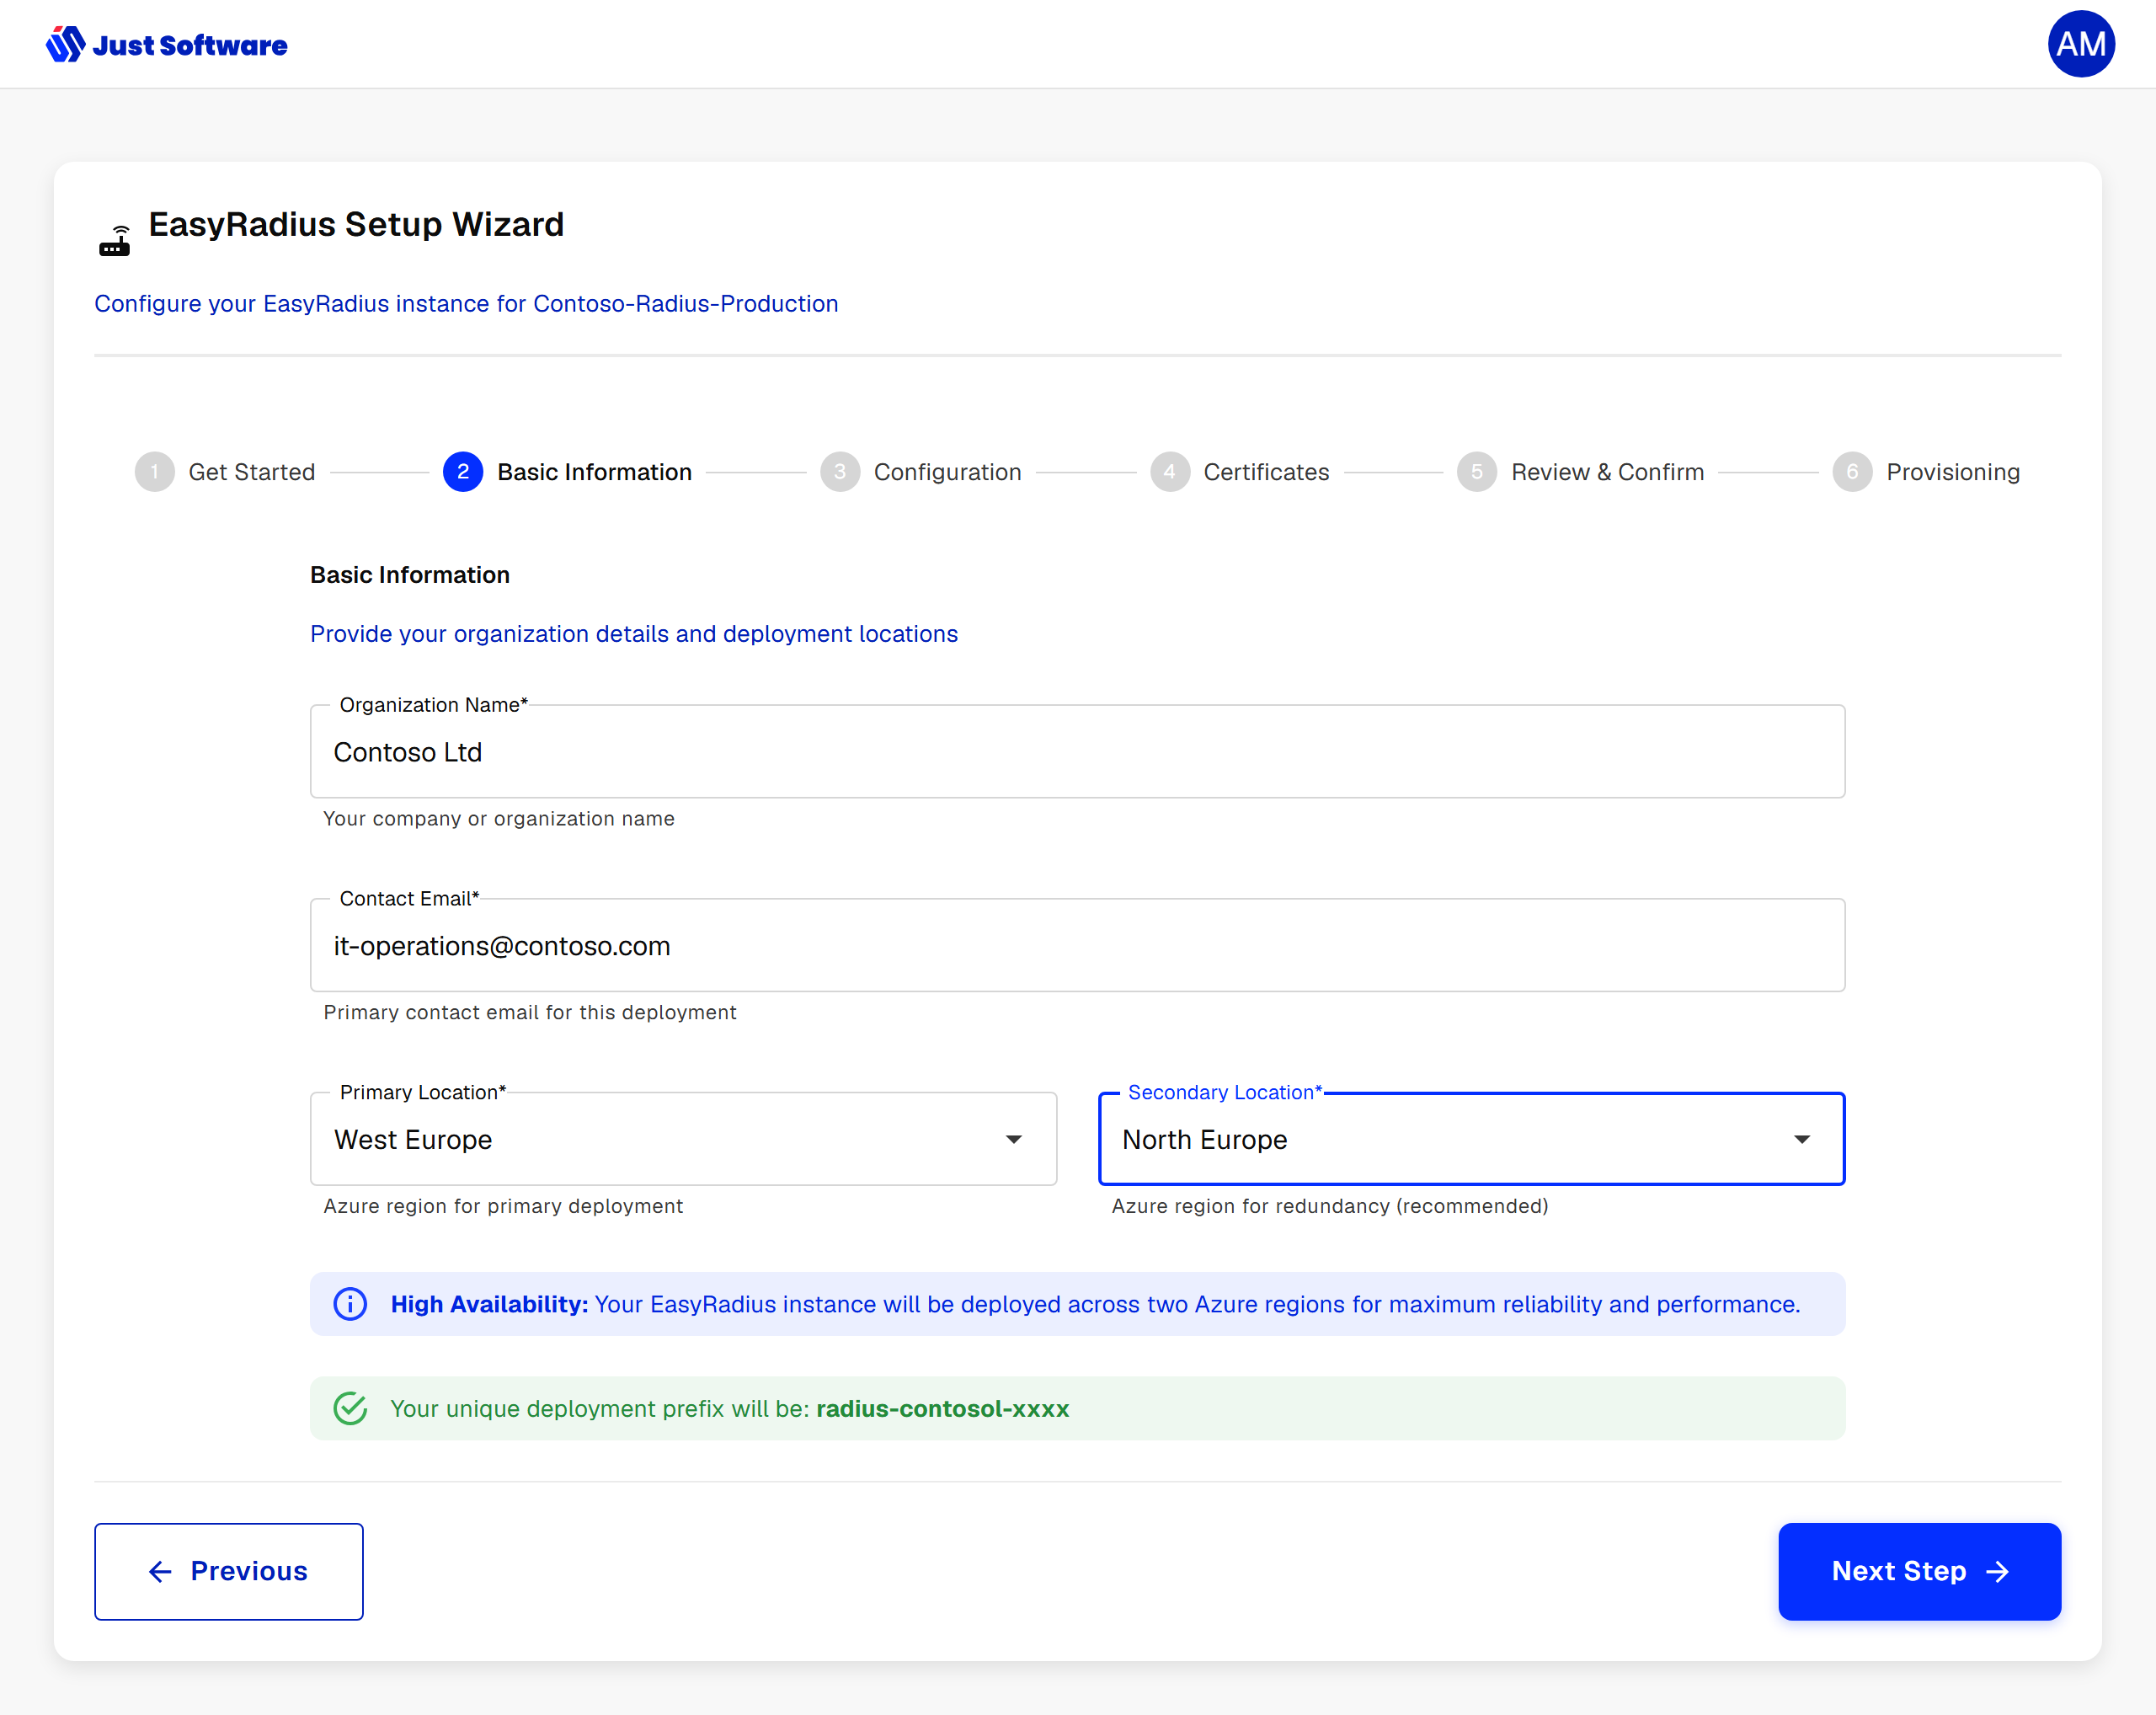
Basic Information. Fill in your organization name and a contact email, and choose a primary and a secondary location. Both are required and they must be different; on plans with high availability, the secondary location runs a second endpoint. We send a confirmation email to the contact address; until it is confirmed, the dashboard shows a reminder.
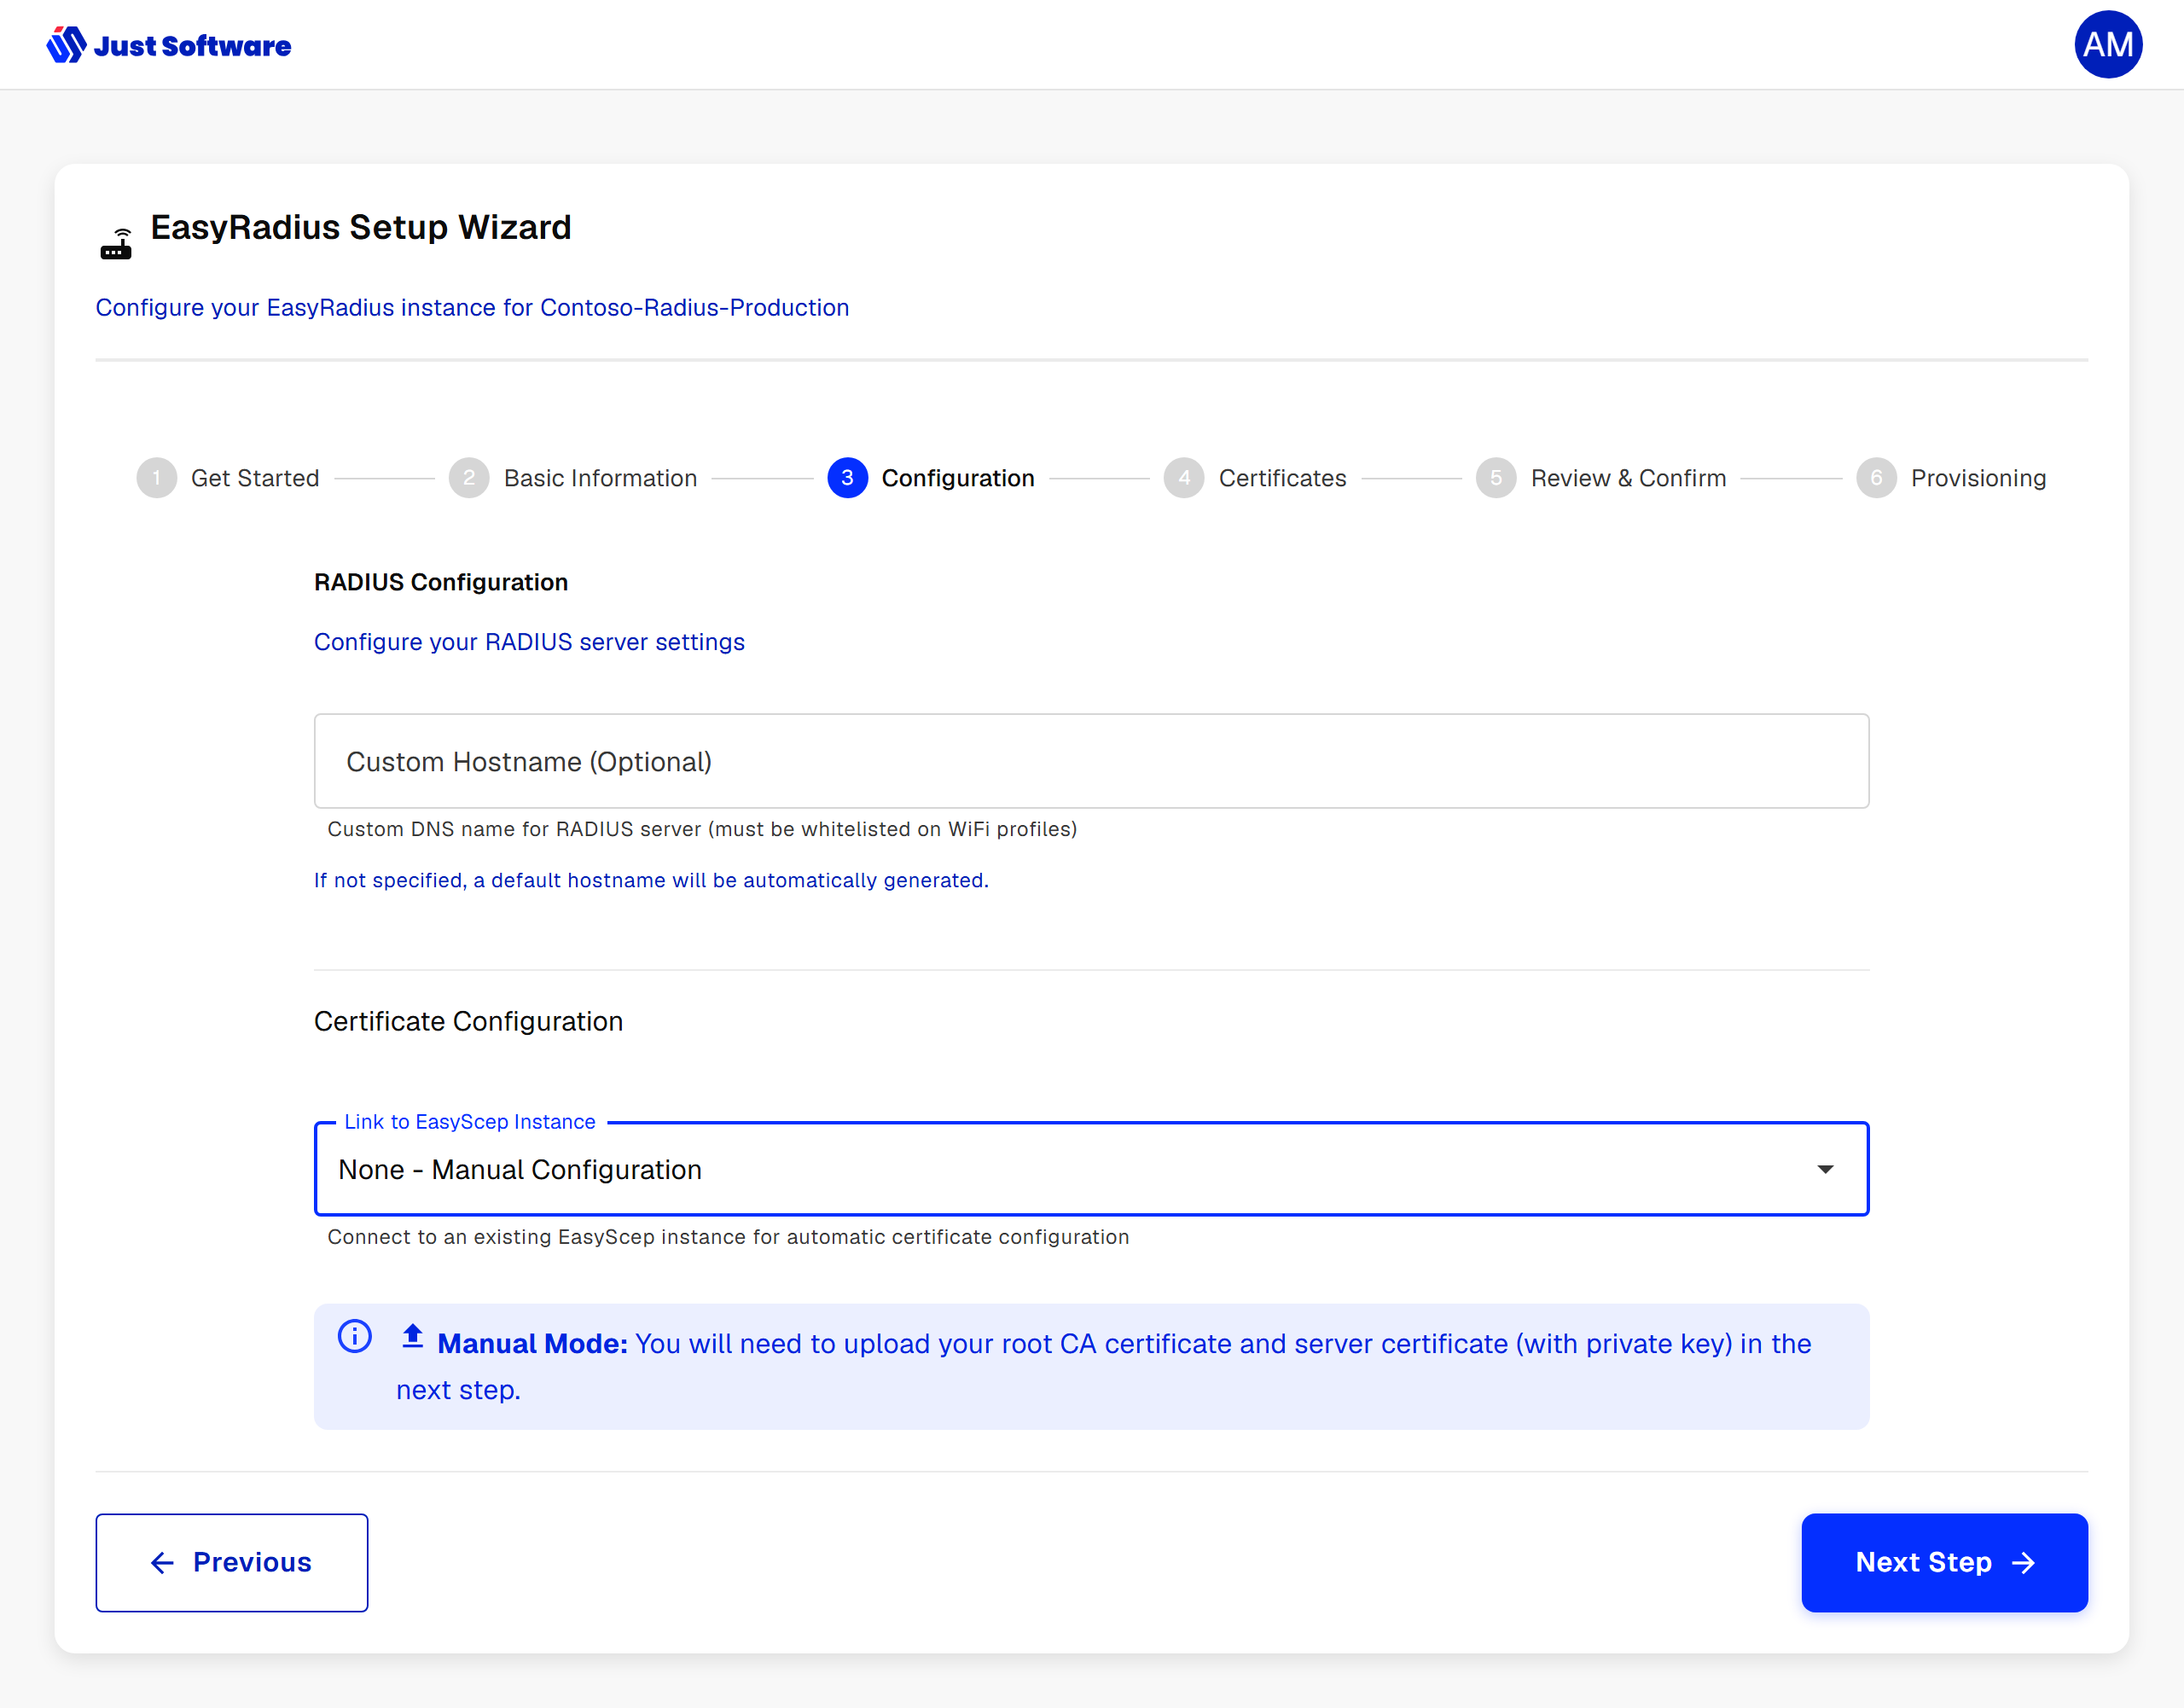
Configuration. Optionally enter a custom hostname for the RADIUS server. If you leave it empty, a hostname is generated for you — if in doubt, leave it empty. If you do set one, you must afterwards create a DNS CNAME record for it, use that name in your Wi-Fi profiles, and use a server certificate that matches it.
Under Link to EasyScep Instance, choose how certificates are handled:
- Your EasyScep instance (listed by its subscription name): EasyRadius trusts your EasyScep root CA and gets its server certificate from EasyScep, including renewal. The certificate upload step is skipped.
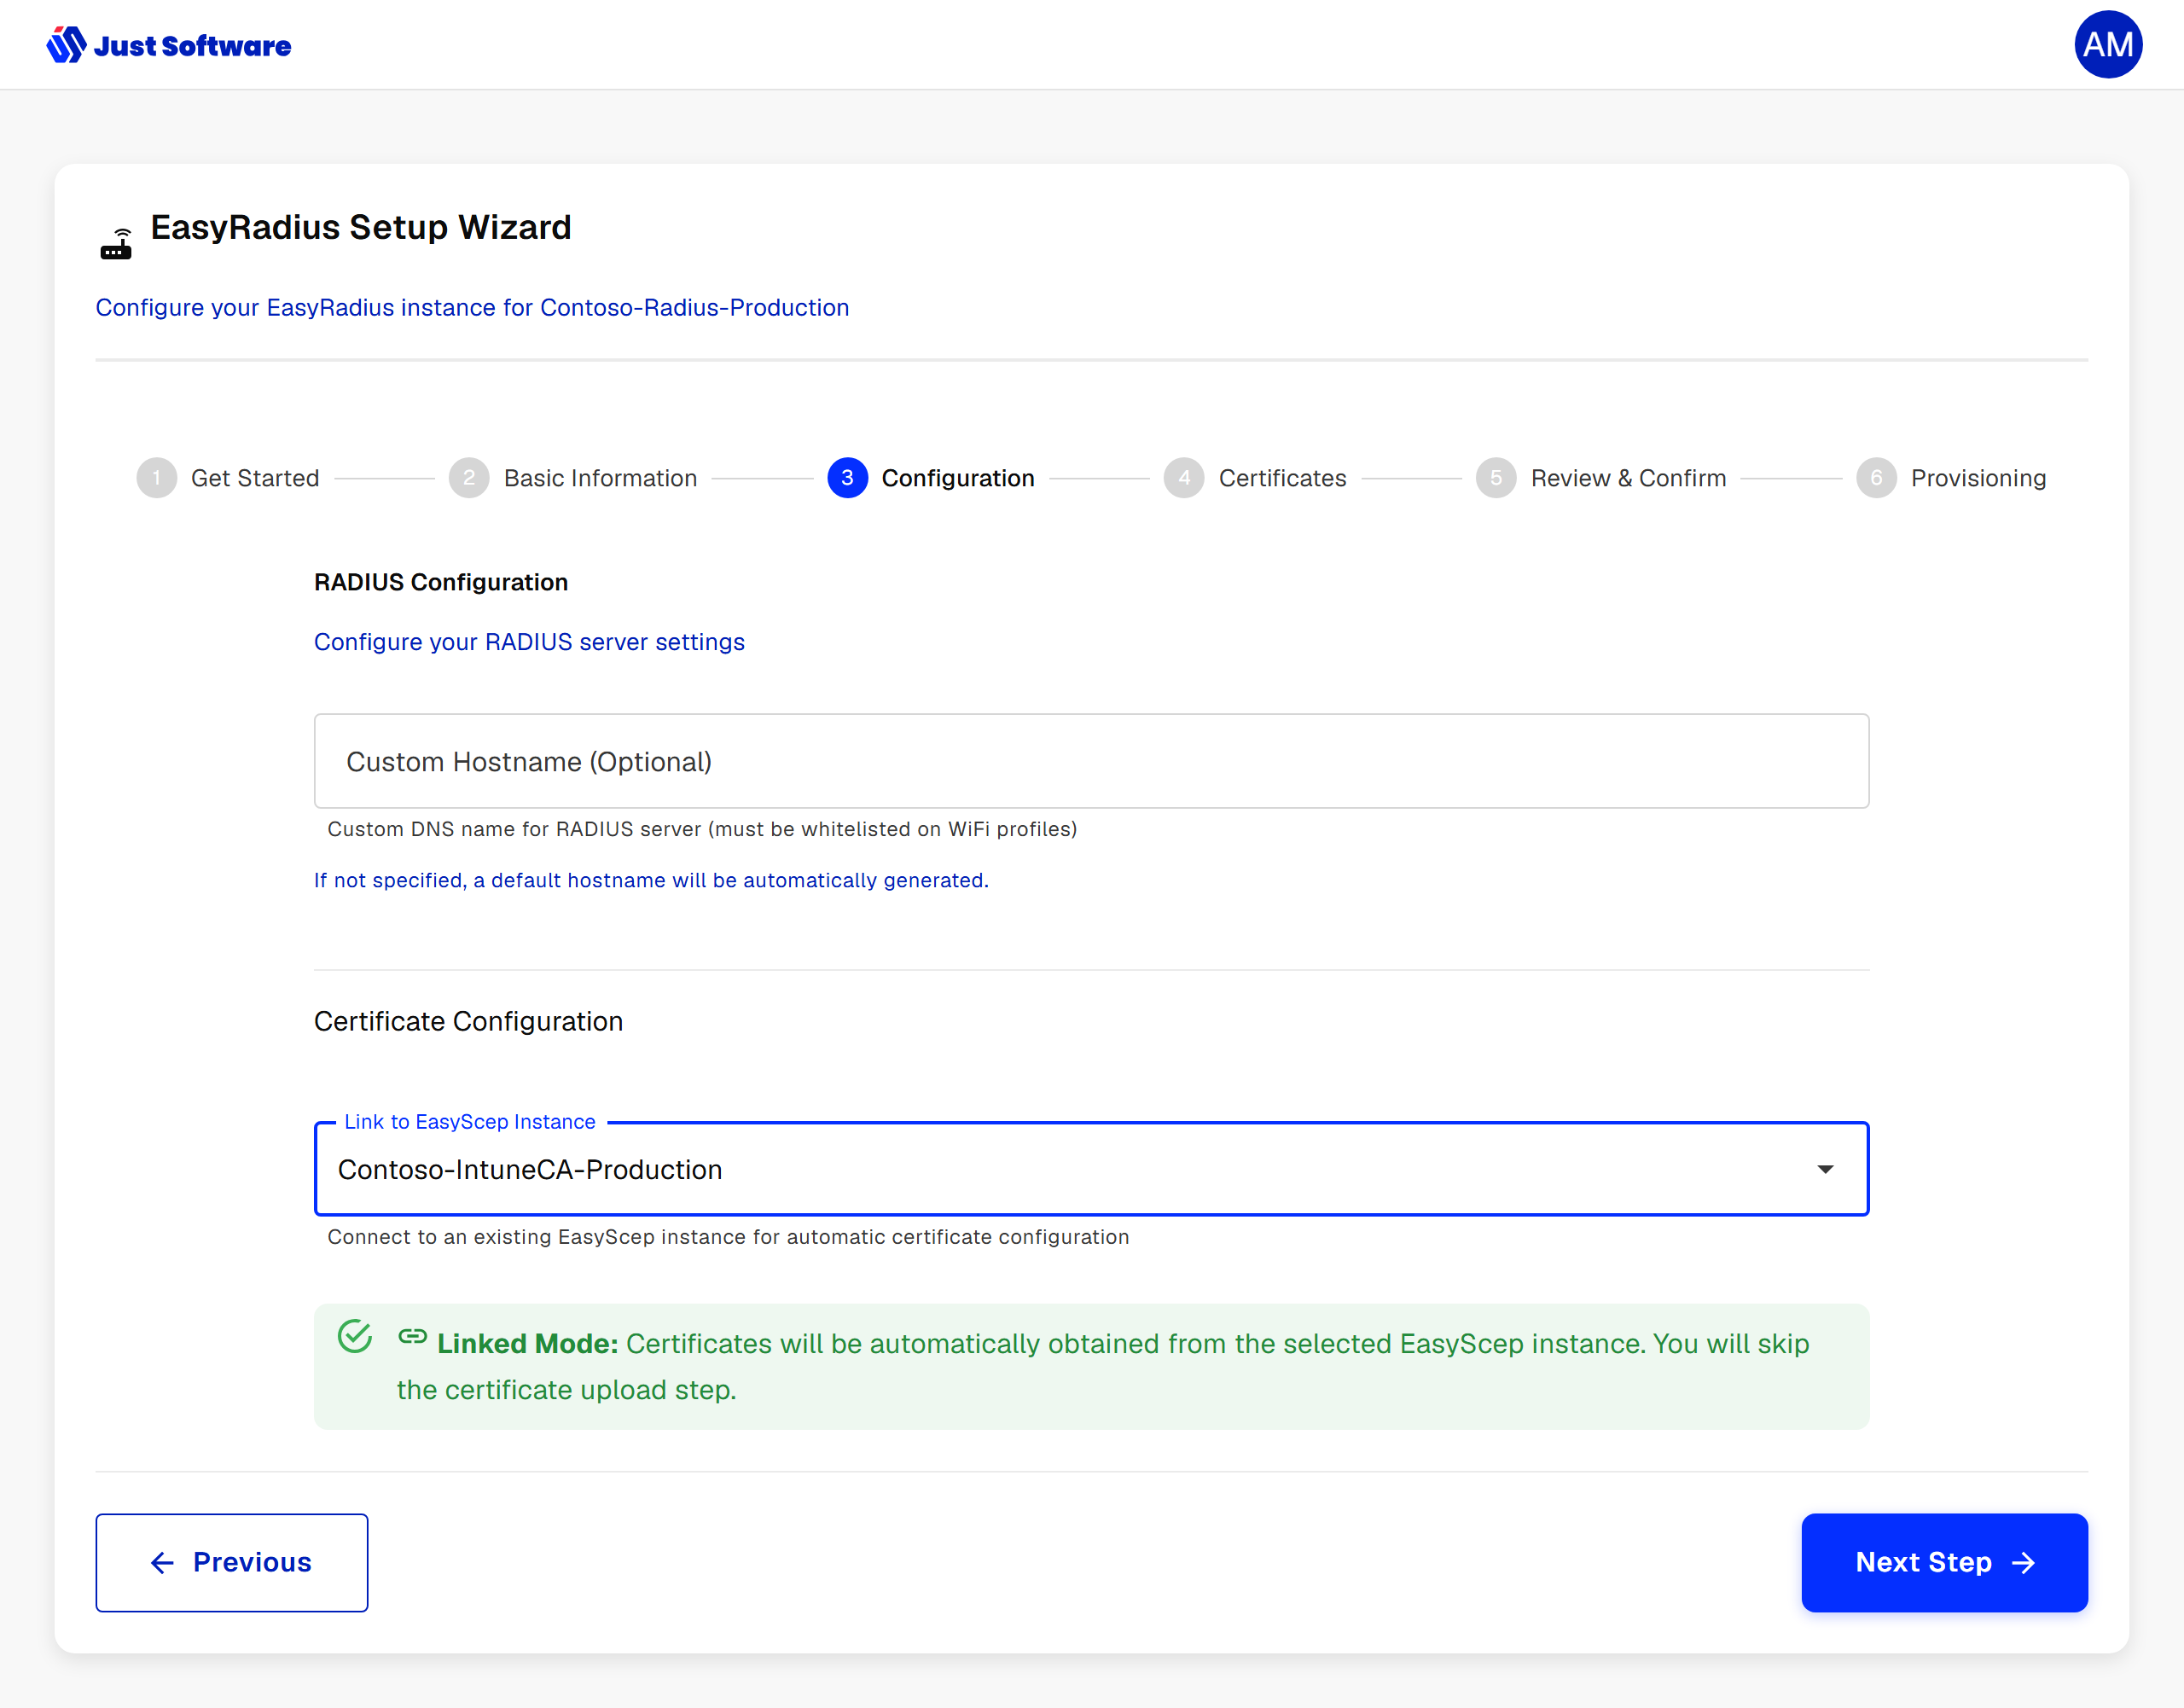
- None - Manual Configuration: you upload the certificates yourself in the next step.
Certificates (manual configuration only). Upload both certificates:
| Certificate | Requirements |
|---|---|
| Root CA Certificate | .cer, .crt or .pem format, must not contain a private key, max 1 MB |
| Server Certificate with Private Key | .pfx or .p12 format, must contain a private key, max 1 MB. If the file is password-protected, enter the password before choosing the file. |
Both certificates must be uploaded before you can continue.
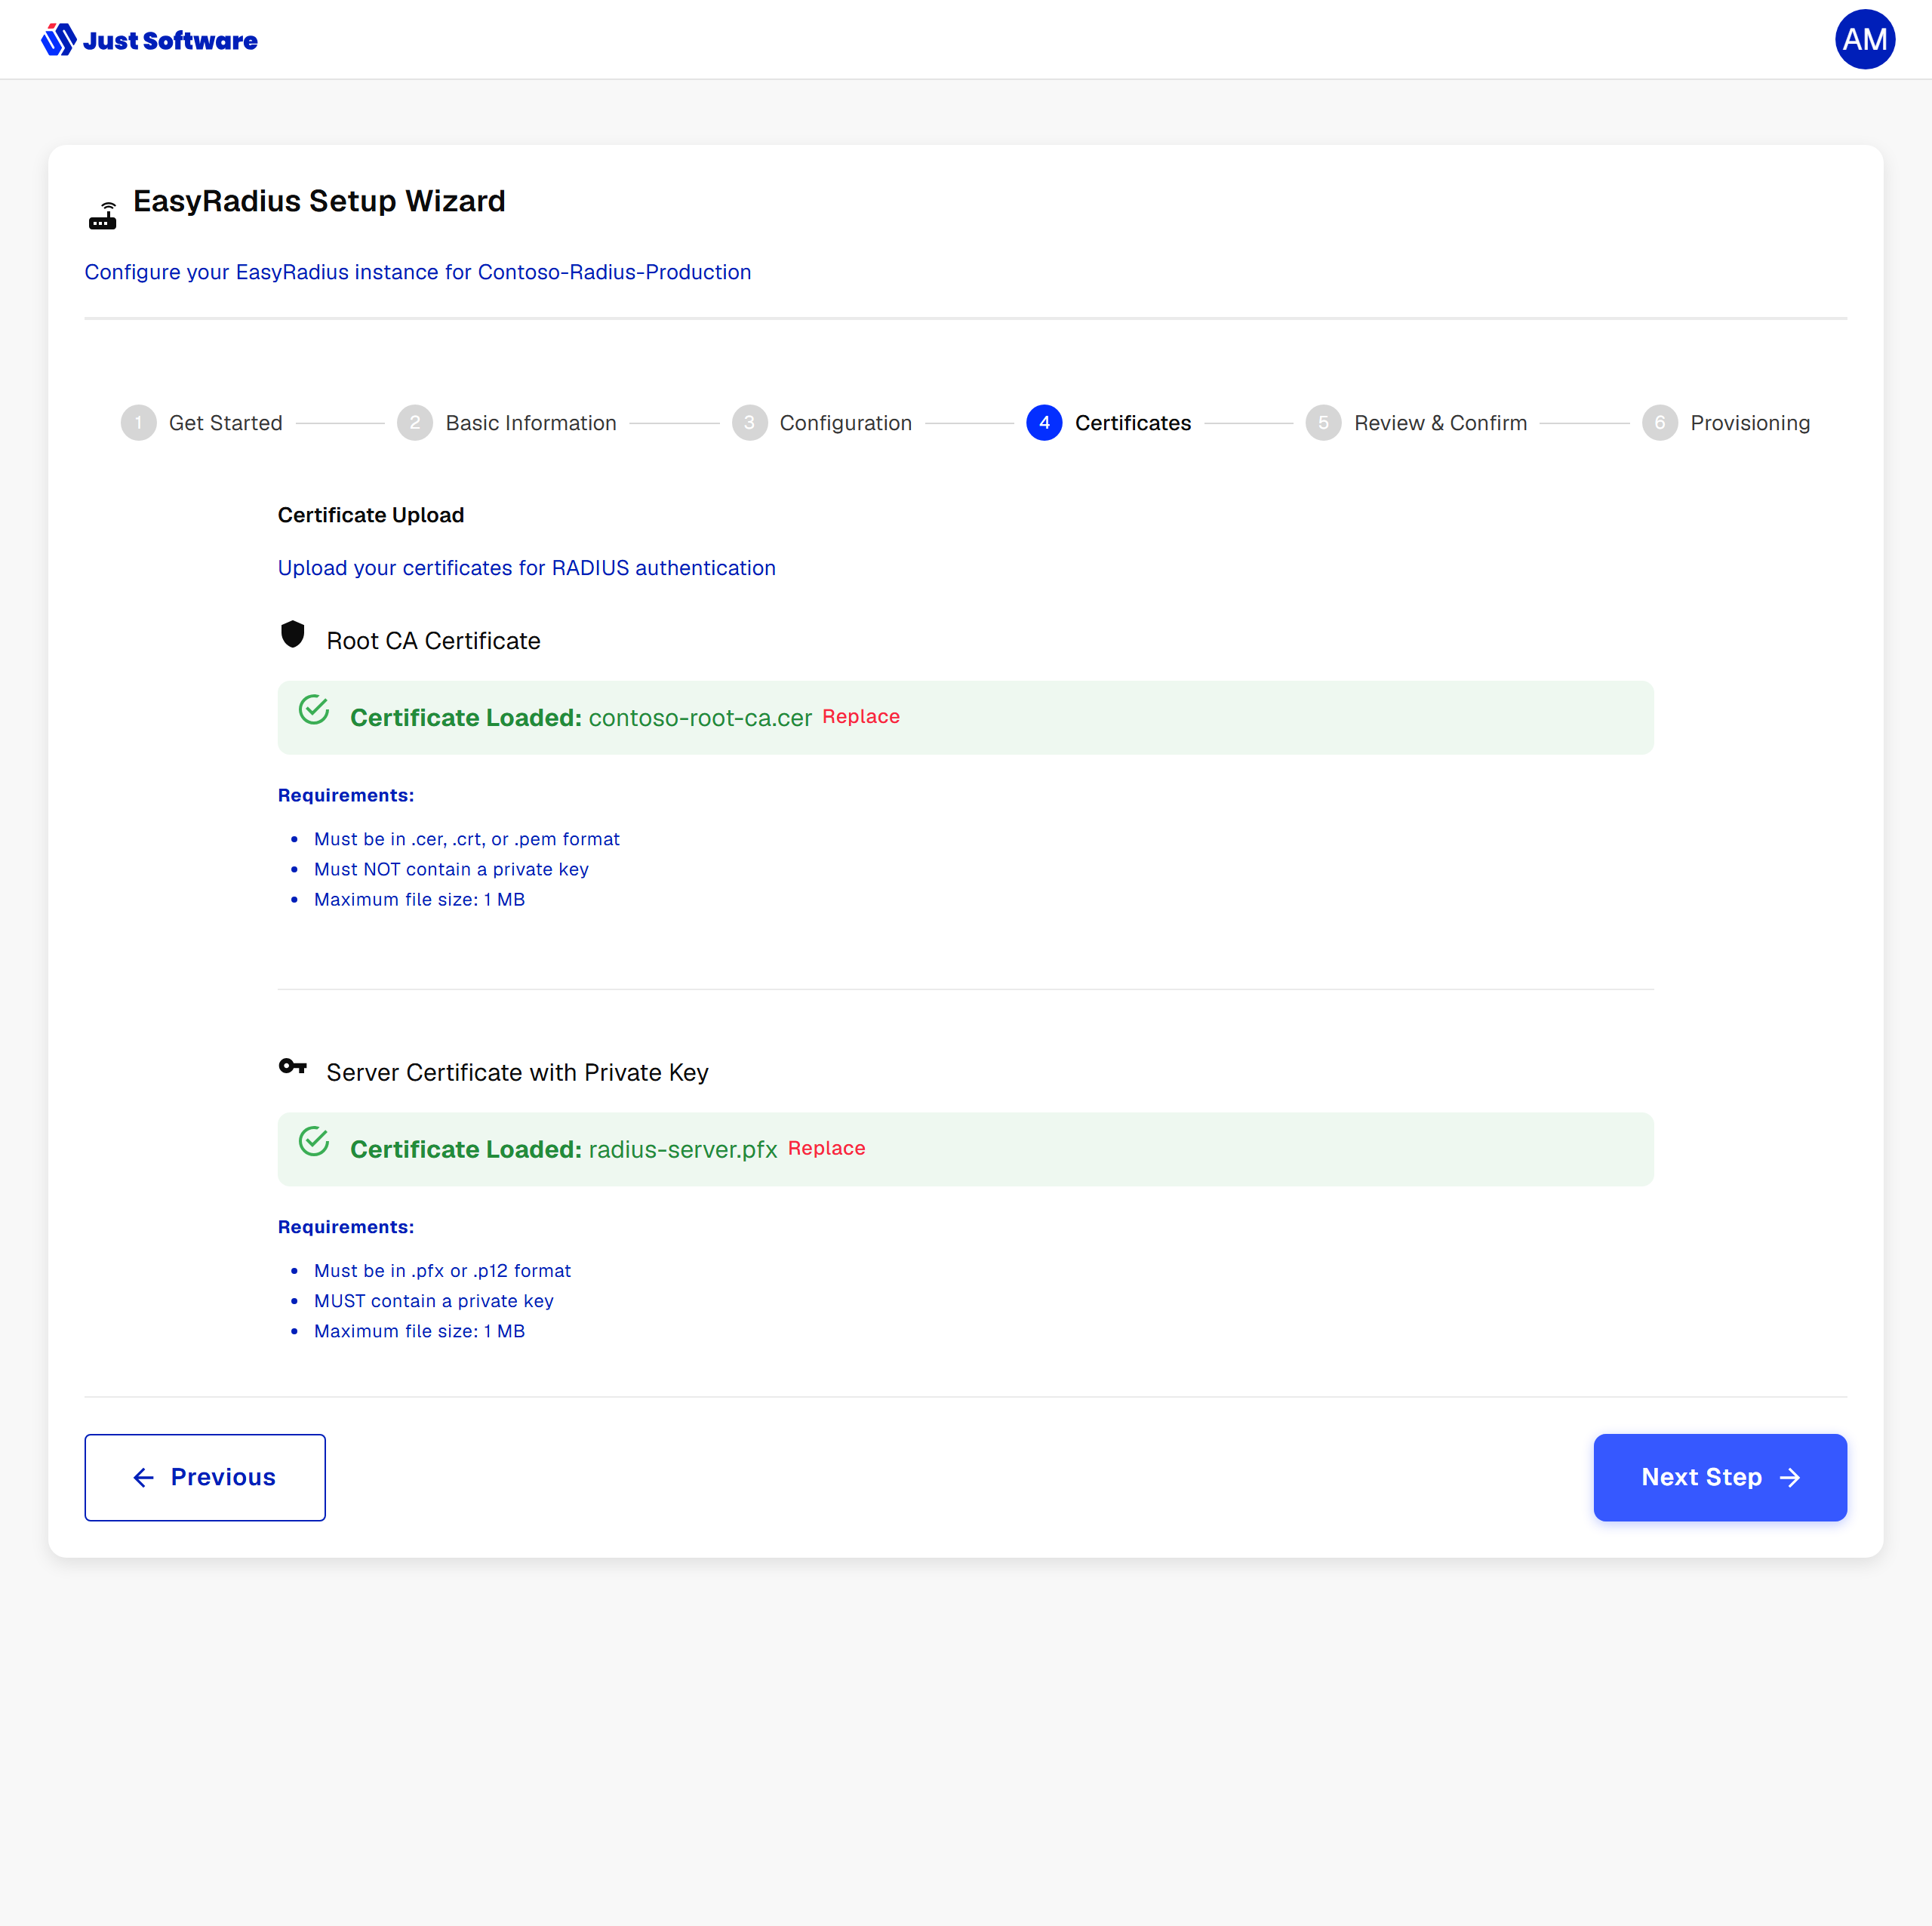
Note: In manual mode EasyRadius does not renew the server certificate for you. Replace it on the Certificates page before it expires — the page warns you 30 days ahead.
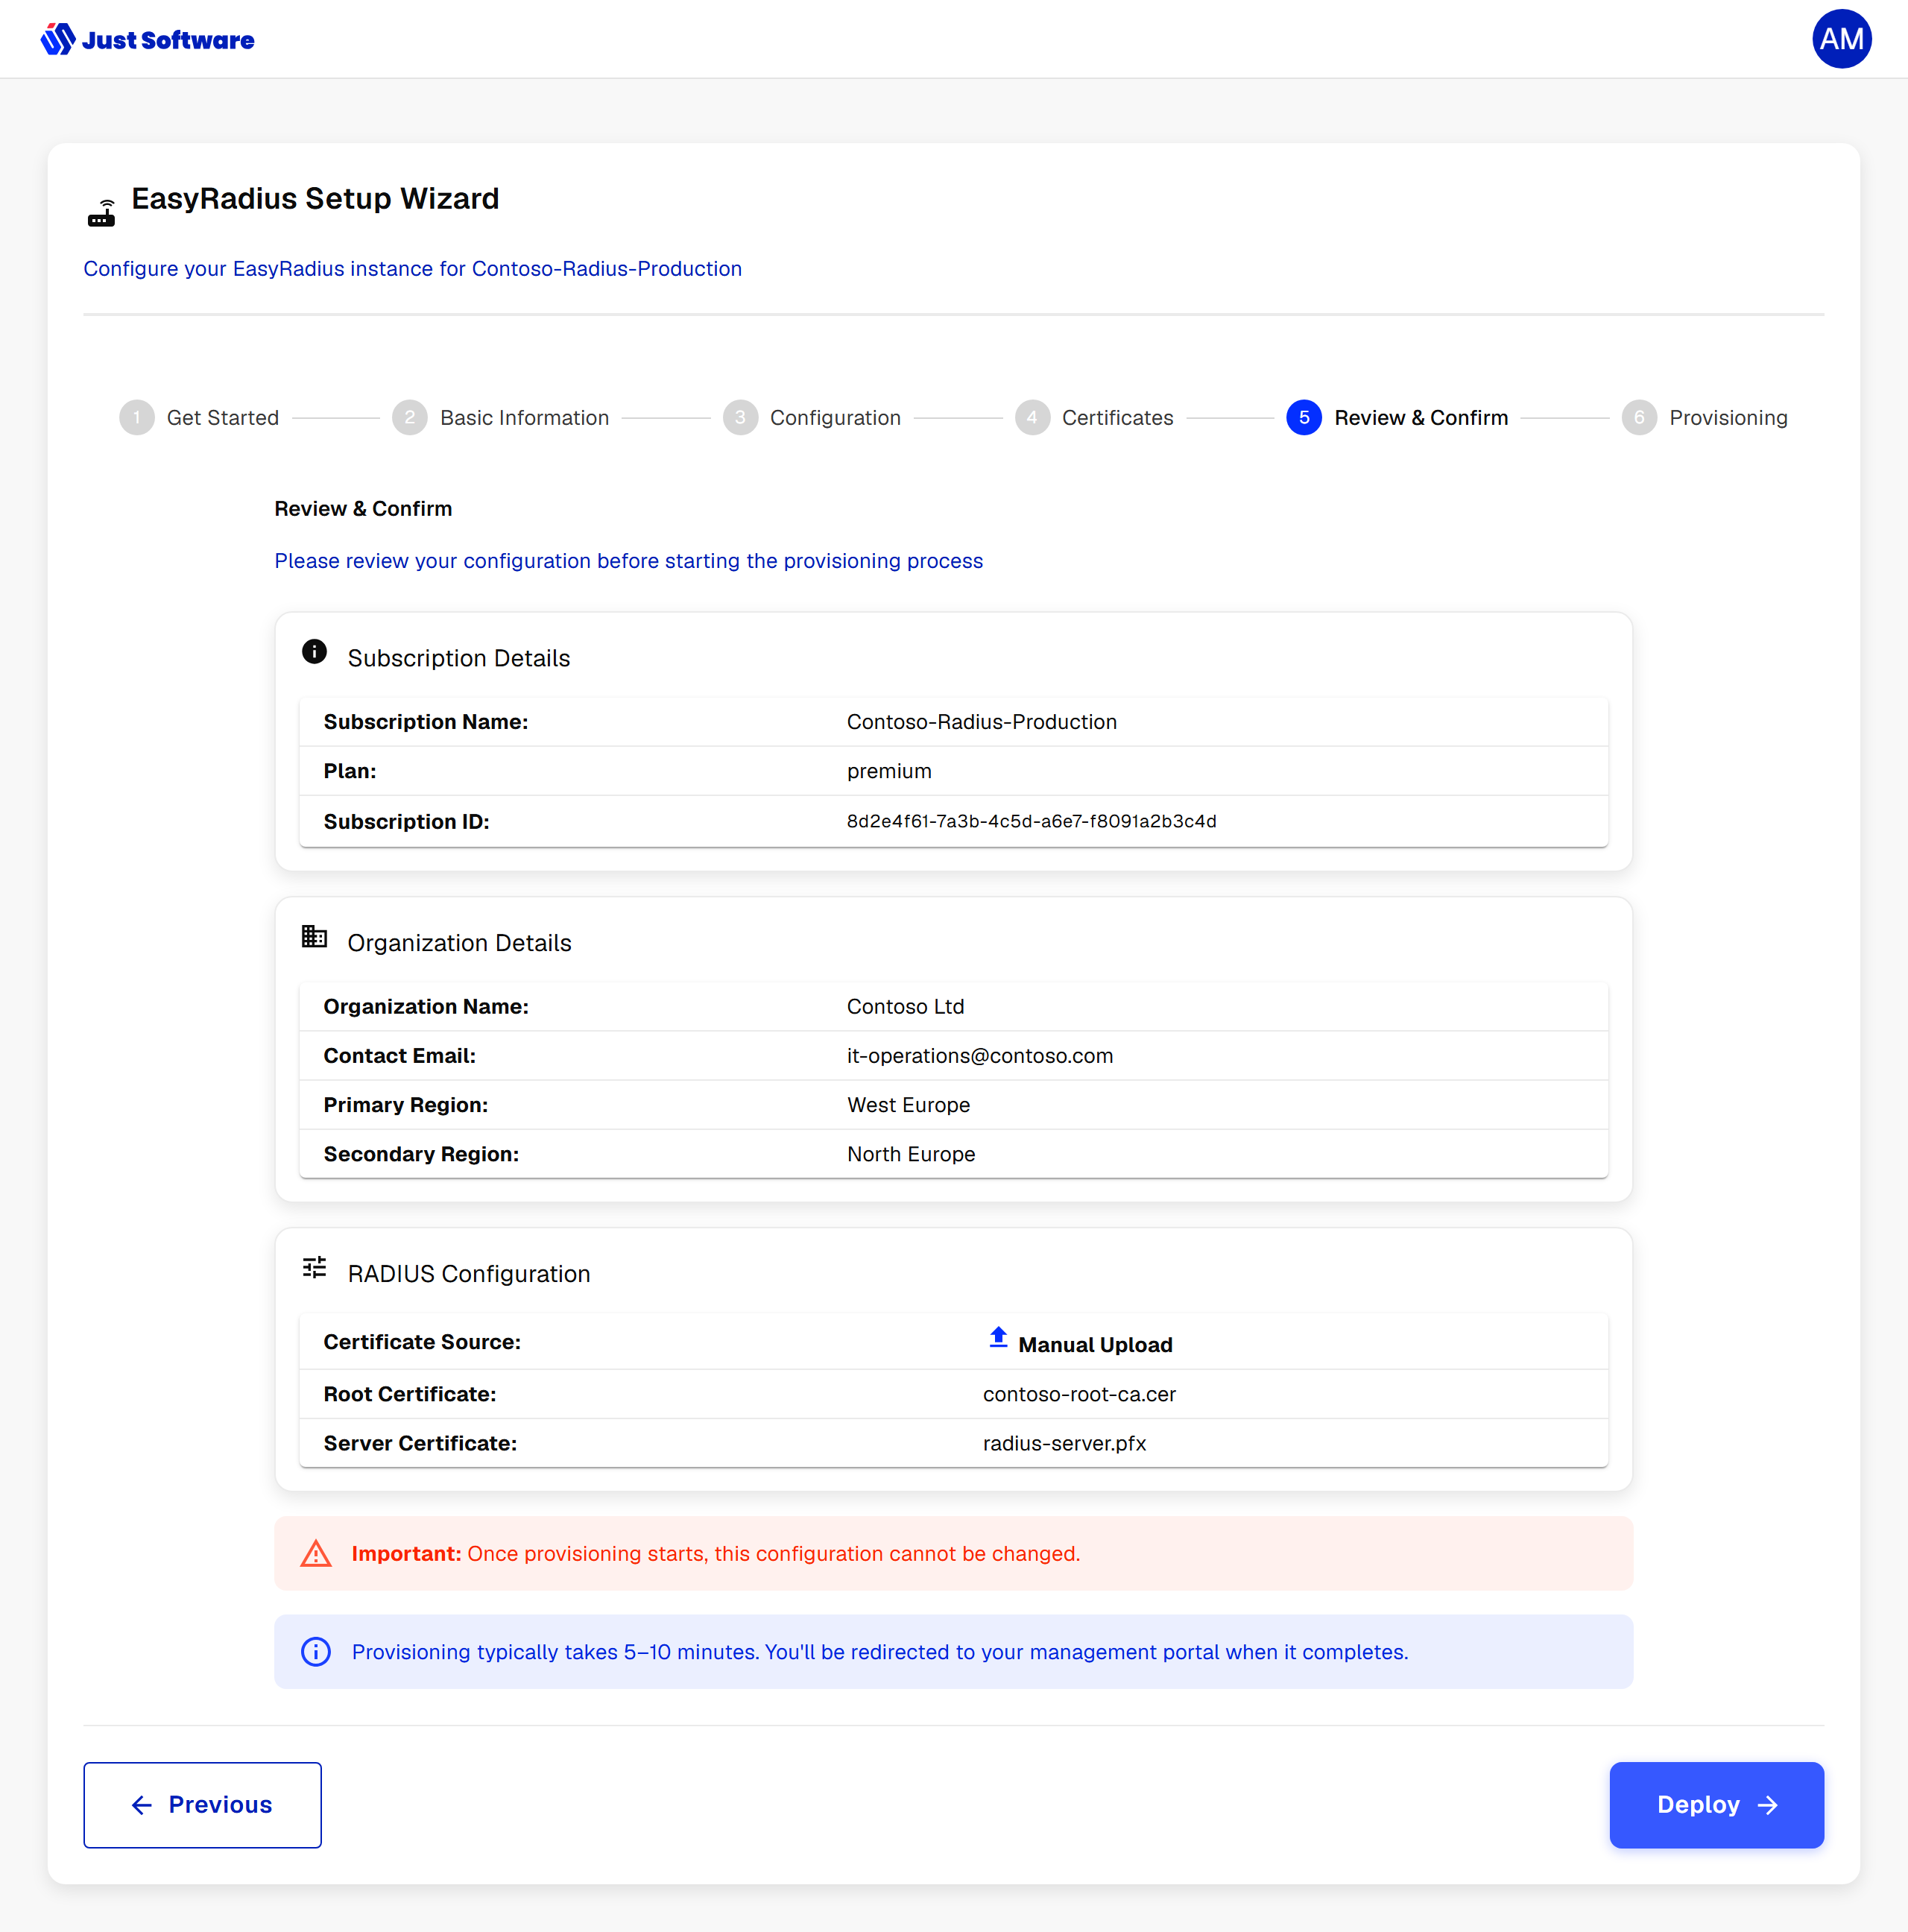
Review & Confirm. Check the summary and click Deploy. The configuration cannot be changed once provisioning starts.
Provisioning. Provisioning typically takes 5–10 minutes. You can close the page and come back later; when provisioning completes you are taken to the EasyRadius administration portal.
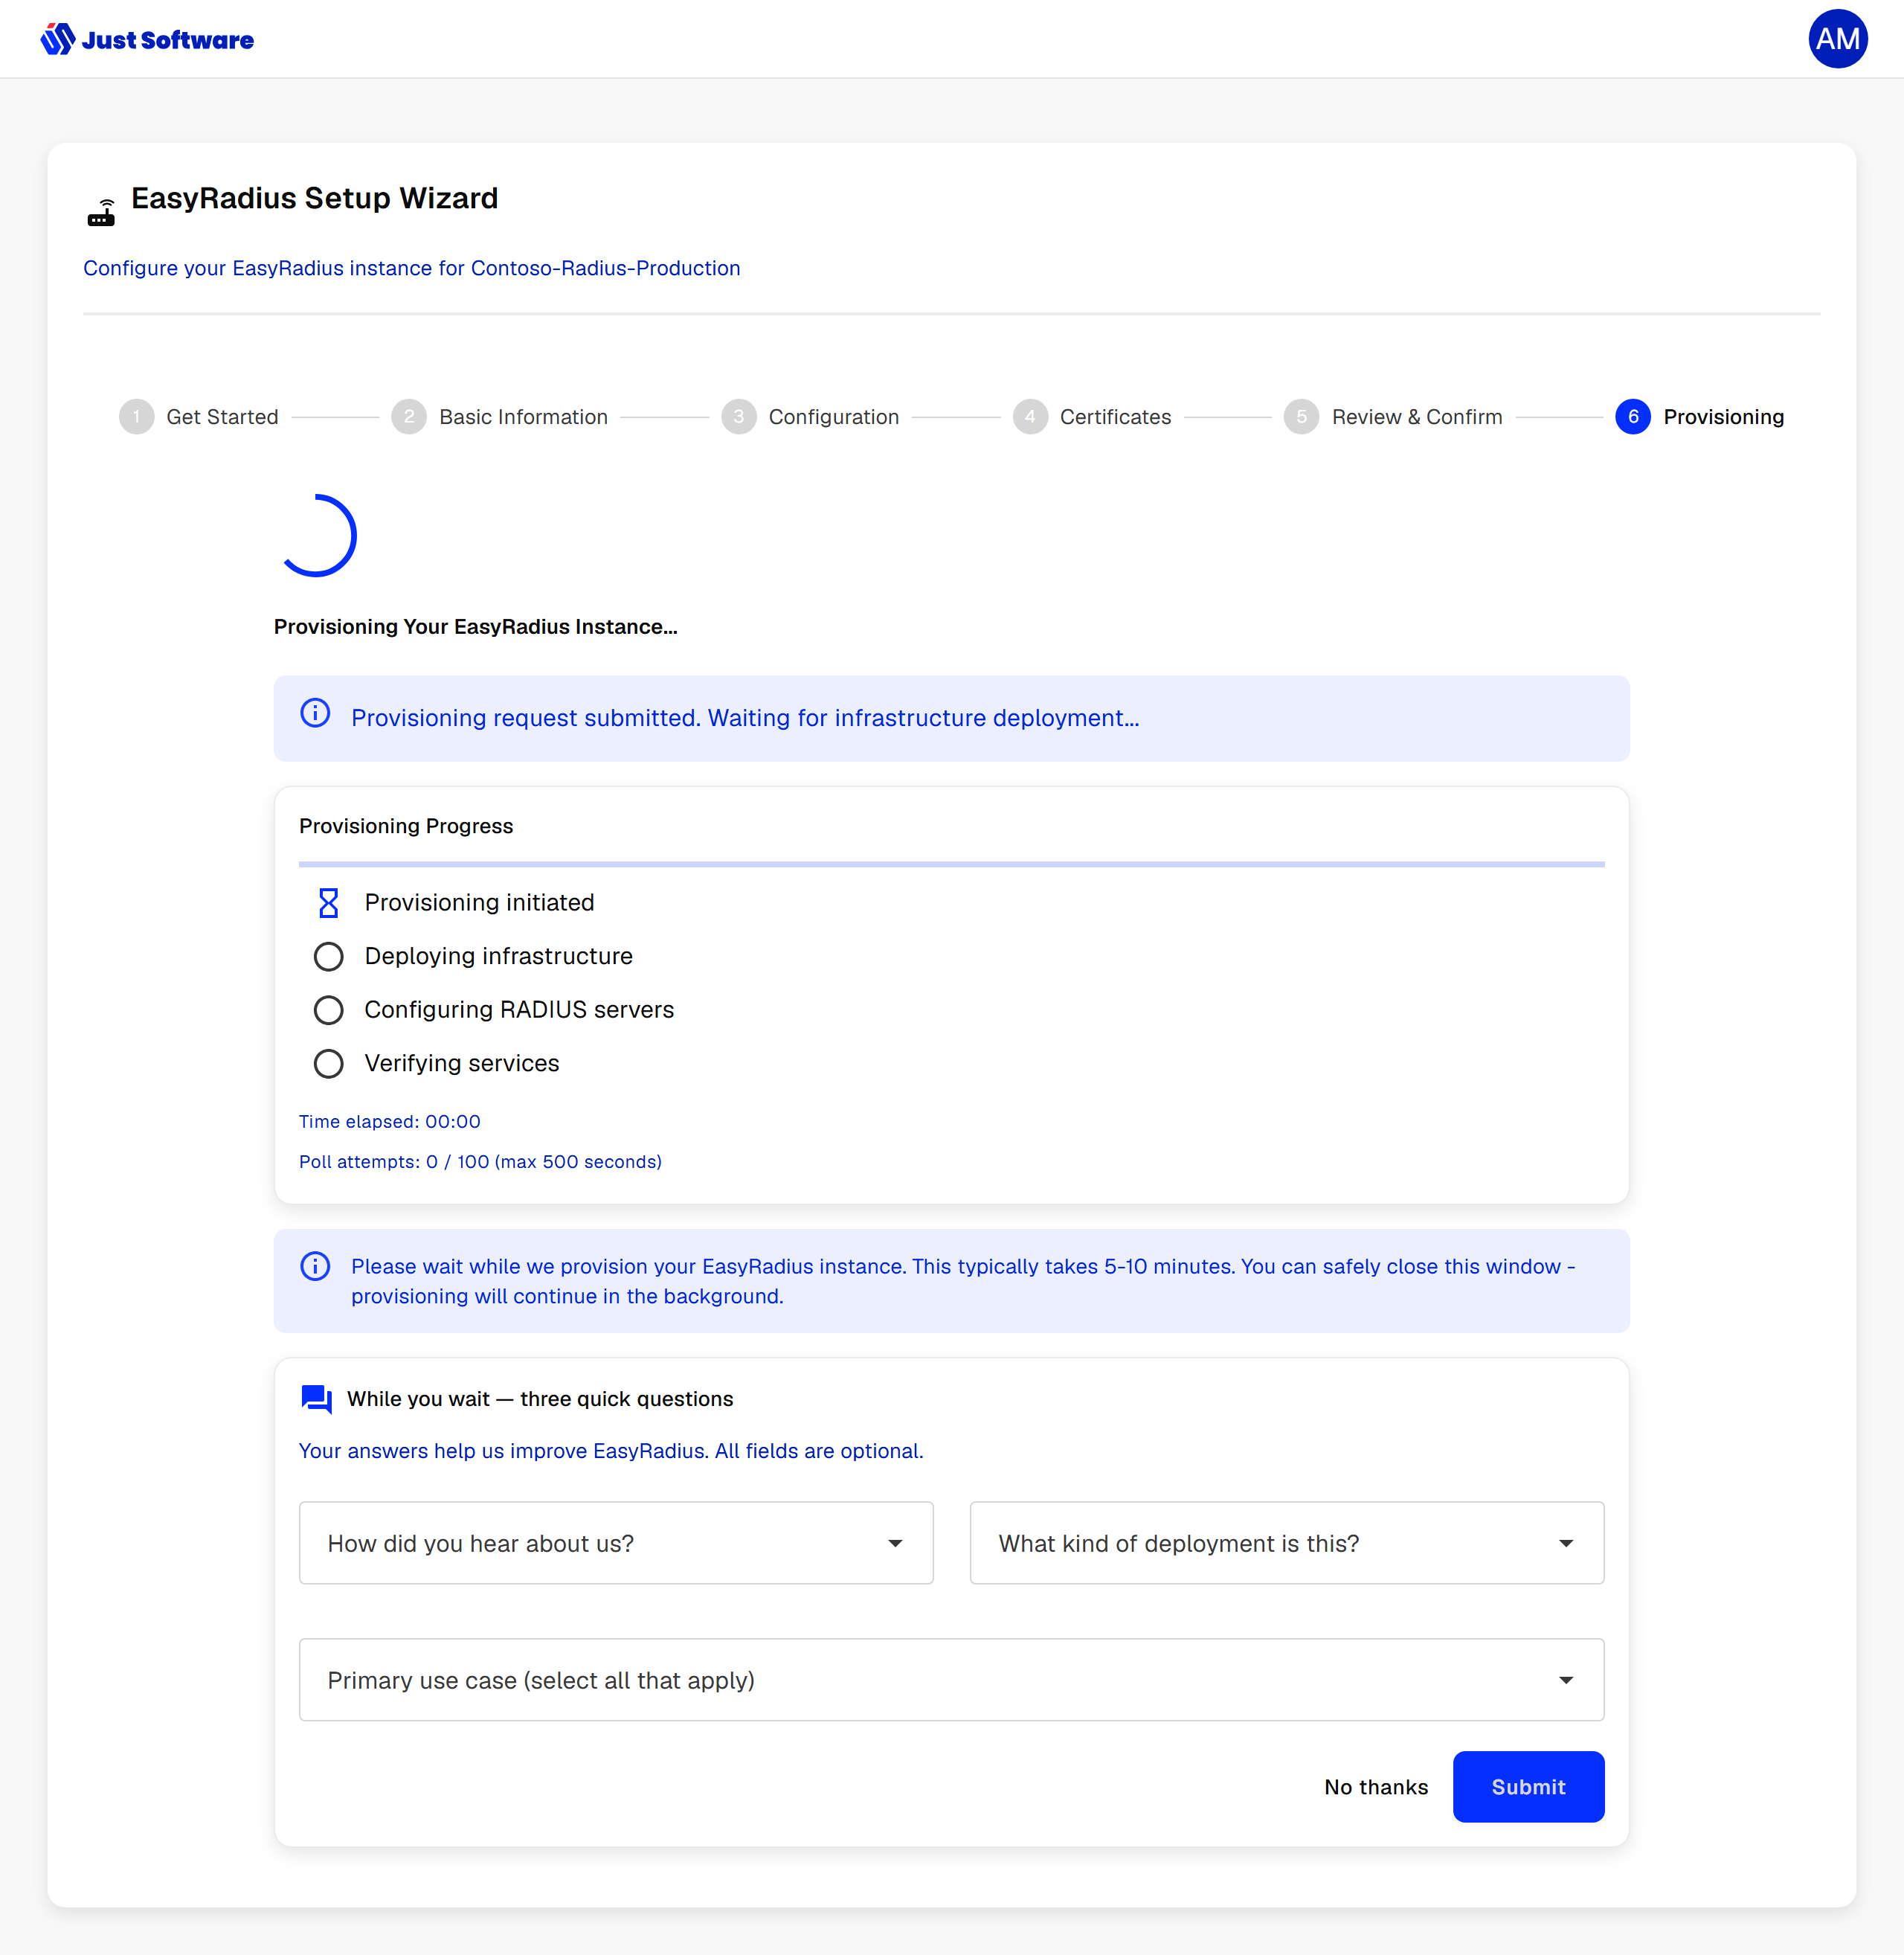
If you close the window, you can always access it again from the Azure Portal, just search for "SaaS" and you can see all your SaaS subscriptions, including your EasyRadius instances. You can also go to the administration portal directly at https://portal.just-software.com at any time.
Verifying your setup
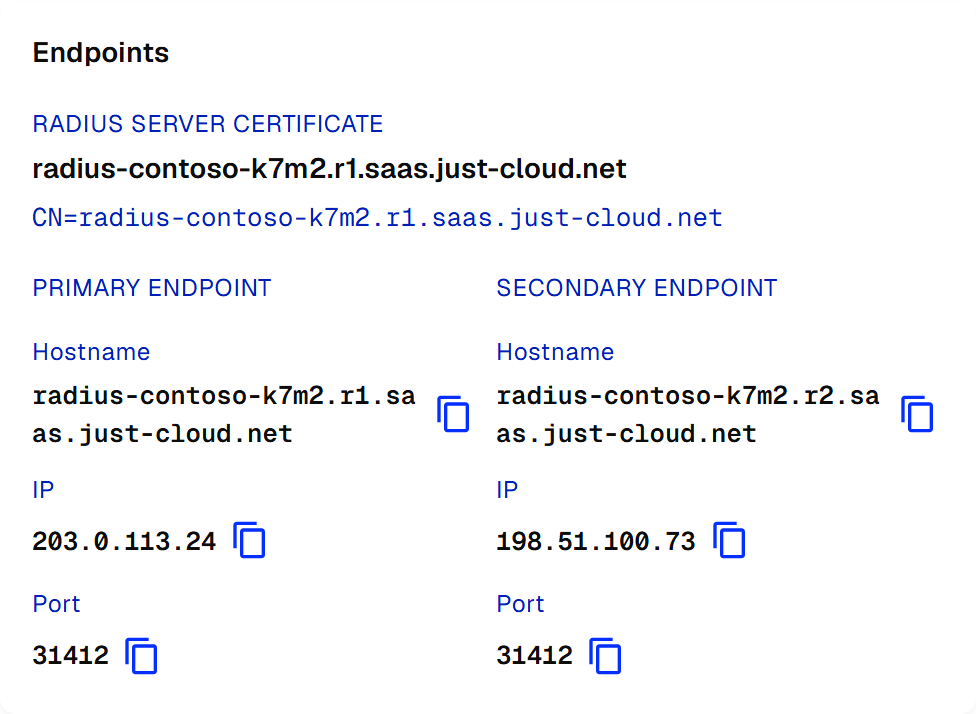
The Dashboard shows the service status and, under Endpoints, everything your network equipment needs: the hostname, IP address and port of both the primary and the secondary endpoint, and the name on the RADIUS server certificate.
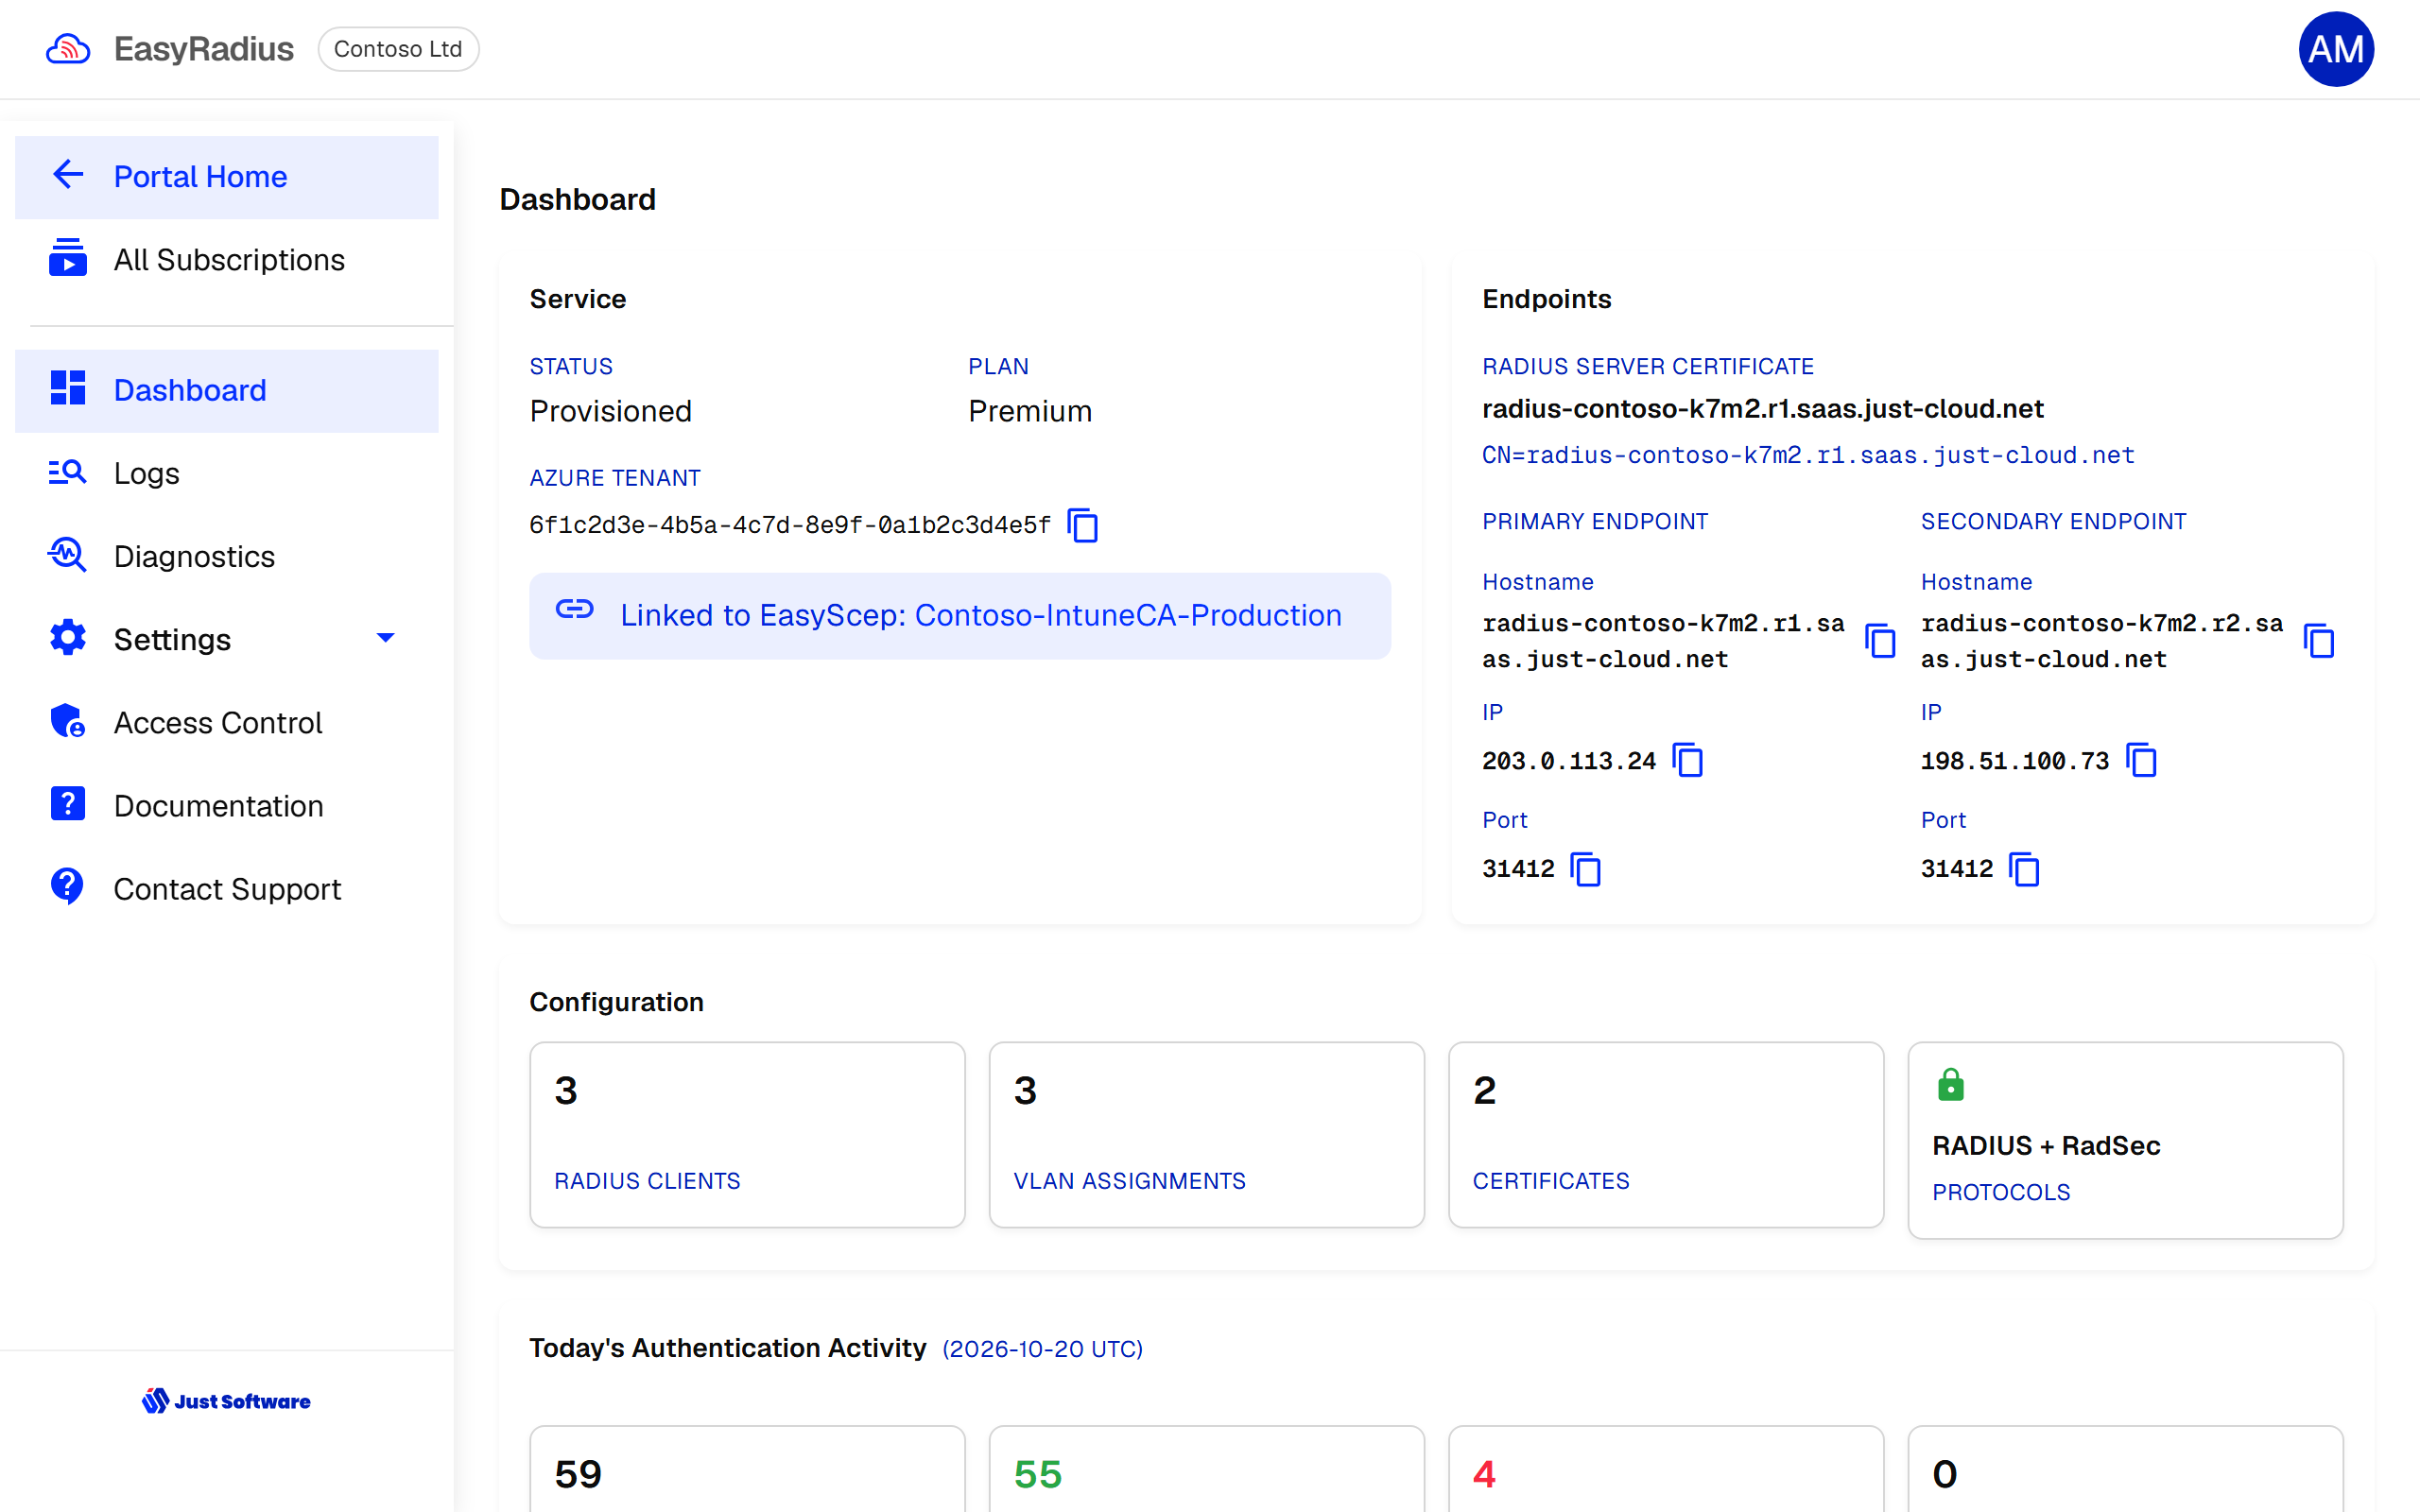
Important: The port is assigned to your instance and is not the standard RADIUS port 1812. Always copy it from the dashboard.
Next steps
- Add your RADIUS clients. Authentication requests are rejected until at least one client is defined. Under Settings → Radius Clients, add an entry for each access point, controller or switch with the public IP address (or network, or hostname) it connects from and a shared secret. See RADIUS clients.
- Choose the protocols your equipment uses — RADIUS over UDP, RadSec over TLS, or both — under Settings → System. See Protocols and ports.
- Open your firewall for outbound traffic from your network equipment to both endpoints on the ports shown on the dashboard.
- Configure your network equipment with both endpoints, so authentication continues through the secondary region if the primary is unavailable. See the UniFi guide for an example.
- Deploy the Wi-Fi profile to your devices. See Intune Wi-Fi EAP-TLS Setup.